TrustCaptcha and BFSG compliance
TrustCaptcha is an invisible CAPTCHA that protects logins, signup forms, checkouts, password resets and APIs from automated abuse. Visitors get no puzzle: the widget starts on its own and runs its check in the background. The verification step therefore adds no barrier to the journeys that BFSG (Barrierefreiheitsstärkungsgesetz) and the European Accessibility Act (EAA) cover.
External reference: BFSG overview (German government)
What BFSG is and why CAPTCHAs matter
BFSG sets accessibility requirements for certain consumer products and services. For digital services, two points follow from it:
- If your service is in scope, people need to be able to complete key journeys (register, log in, buy, request support) using assistive technology and common accessibility settings.
- If your anti-bot layer blocks those journeys, that is an accessibility problem, however secure the layer is.
BFSG vs. EAA
BFSG is the German law that transposes the European Accessibility Act (Directive (EU) 2019/882). The directive has been in force since 2019, and both have applied since 28 June 2025. In practice, teams meet the requirements through recognized standards and testable criteria.
Where traditional CAPTCHAs usually break accessibility
CAPTCHA problems tend to show up when users try to finish a critical action:
- Login, MFA enrollment, password reset
- Registration and account verification
- Checkout and payment flows
- Contact/support forms, quote requests, appointment booking
The verification step is part of these flows, so it has to be accessible along with the rest.
Who BFSG applies to
Whether you’re in scope depends on the type of service you provide and the market you serve. In practice, BFSG comes up most often for:
- E-commerce / web shops serving consumers
- Banking and payment user journeys
- Telecom and digital communications
- Passenger transport and ticketing-related digital services
- Consumer-facing digital services where accessibility obligations apply
What IT teams should do first
- Identify which offerings are consumer-facing and potentially covered.
- List the critical user journeys (login, signup, checkout, support).
- Check that each journey has an accessible verification and recovery path.
Standards to align with (what auditors and vendors will mention)
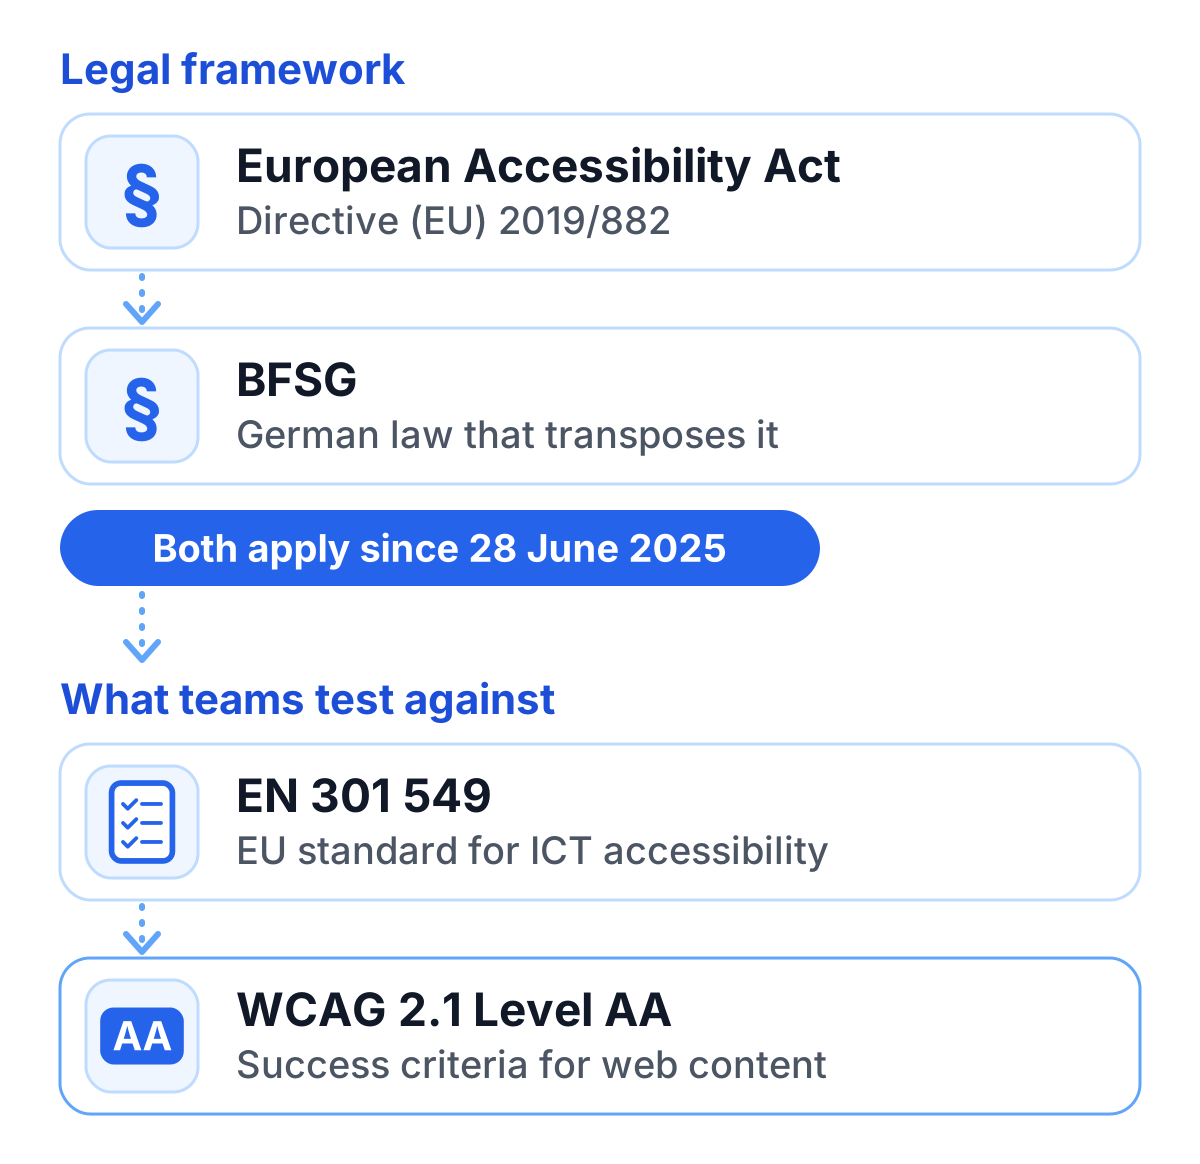
BFSG work usually refers to EN 301 549, the EU standard for ICT accessibility. For web content, the current version of EN 301 549 references the WCAG 2.1 Level AA success criteria. WCAG 2.2 is the current W3C recommendation; our WCAG guide shows how TrustCaptcha maps to it.
For engineering teams, this means your verification layer should be compatible with:
- As few interactions as possible
- Keyboard-only navigation
- Screen readers and accessible name/role/value semantics
- Clear error messaging and recovery
- No time-based failure traps
- Predictable DOM behavior (no hidden focus traps, no inaccessible overlays)
Why traditional puzzle CAPTCHAs fail accessibility
Puzzle CAPTCHAs often create barriers such as:
- Vision dependence: image selection, distorted text, low-contrast visuals
- Audio dependence: noisy “audio CAPTCHA” fallbacks that are hard to understand
- Cognitive load: complex instructions, multi-step puzzles, time pressure
- Motor barriers: precise pointer interactions, drag-and-drop, tiny hit targets
- Failure loops: repeated challenges without a clear alternative path
Even “accessible alternatives” often give unequal access in practice.
TrustCaptcha’s approach to accessibility
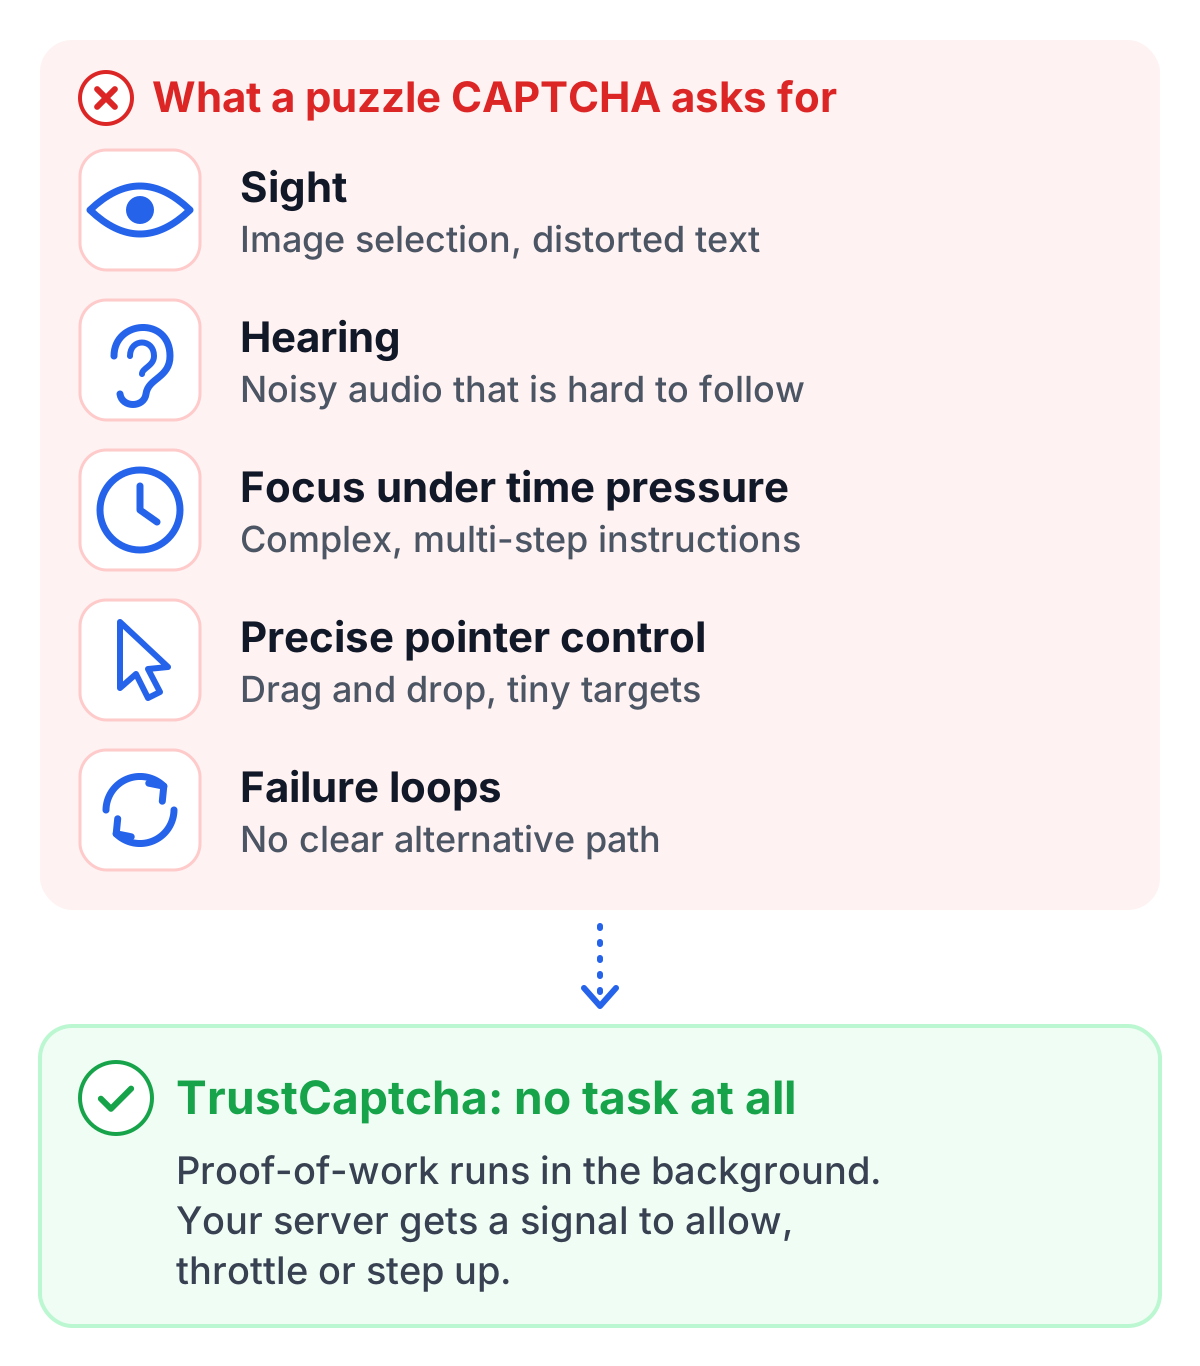
TrustCaptcha avoids the most common CAPTCHA accessibility problems by removing the challenge itself: there is no puzzle to solve in any configuration, and the widget starts on its own.
Invisible, no-interaction verification
TrustCaptcha generates a risk assessment for an interaction. Instead of asking the user to solve a puzzle, your backend receives a decision signal you can use to allow, throttle or step up.
Accessibility benefit: no “prove you’re human” interaction, no puzzle and no audio fallback that users must decode. The widget is visible by default and finishes without any input.
Implementation of TrustCaptcha in BFSG contexts
A practical way to add bot protection while keeping the flow accessible:
Proof-of-work verification (invisible)
Proof-of-work is a small computing task that the visitor’s device solves in the background before a sensitive request is accepted. Real users usually do not notice it. For bots operating at scale (credential stuffing, form spam, scraping, brute force), it raises the cost of every attempt, so high-volume abuse gets slower and more expensive. The server verifies the proof quickly, and the difficulty rises with the risk of the request, so you get strong protection without puzzles or accessibility barriers.
Bot score and automation intelligence per request
For each protected request, TrustCaptcha returns a bot score from 0 (very likely human) to 1 (very likely bot) along with automation indicators that help you identify suspicious traffic. Bot scoring is included from the Solo plan. Instead of a binary “pass/fail CAPTCHA”, your backend receives a score you can use for policy decisions such as allow, rate-limit, step-up or block, and to log security-relevant context for incident response.
Typical outputs teams use include:
- Allow
- Allow with monitoring
- Step-up
- Reject (rare, ideally only for clear automation)
Accessibility note: For BFSG-aligned flows, step-up should remain accessible (e.g., email OTP, magic link, support path). Avoid puzzle-based challenges or complex flows that can exclude users.
How the bot score can be used to support BFSG compliance
Consider a policy matrix. A higher bot score means a request is more likely automated, and 0.5 is the recommended starting threshold. The score ranges below are an example:
| Risk level | Example response | Accessibility note |
|---|---|---|
| Low (bot score below 0.3) | Allow | No interaction added |
| Medium (0.3 to 0.5) | Allow + rate-limit | Invisible to user |
| Elevated (0.5 to 0.7) | Step-up (email OTP) | Provide clear instructions, no puzzle |
| High (above 0.7) | Temporary block + retry | Provide accessible message + alternative |
Avoid these integration mistakes
- Blocking the user with a modal overlay that traps focus
- Using timeouts that reset forms without warning
- Returning generic messages with no next step
- Requiring pointer-only interactions to proceed
UX requirements and user messaging
The wording in your UI affects both usability and accessibility:
- Use plain language
- Give a clear next step
- Preserve user input when possible (e.g. save progress in the form)
- Make sure messages are announced to assistive tech (ARIA live regions or equivalent patterns)
Testing checklist for BFSG readiness
Use this checklist when you evaluate a CAPTCHA setup for BFSG.
Keyboard-only
- I can complete the full flow using Tab / Shift+Tab / Enter / Space / Arrow keys only.
- The focus indicator is always visible.
- Focus order is logical (top-to-bottom, left-to-right).
- No focus traps (I can always move focus forward/backward and exit dialogs).
- Any modal/dialog can be closed with keyboard and returns focus to a sensible element.
Screen reader support
- Inputs have an associated label (or programmatic accessible name).
- Required fields are announced as required.
- Errors are announced when they appear (e.g., via ARIA live region or equivalent).
- Error messages clearly identify the field and the fix (not just “invalid”).
- Buttons/links have meaningful names.
- Status messages are announced.
Zoom, reflow, and large text
- At 200% zoom, the flow is still usable (no hidden buttons, no clipped text).
- Layout reflows without horizontal scrolling on common viewport sizes.
- With large text settings (OS/browser), labels and errors remain readable and aligned.
- Tap targets remain usable on mobile (no tiny hit areas).
Contrast and readability
- Text meets contrast expectations (including placeholder/help text).
- Focus outline/indicator remains visible at all times.
- Error states (red borders, icons) include text, not color-only meaning.
- CAPTCHA states are distinguishable.
Timeouts and retry behavior
- If there is a timeout, users get a clear warning and a way to extend/retry.
- A timeout does not silently reset the form or lose user input without notice.
- Retrying does not send users into an endless loop.
- Rate limits/throttles return a human-readable message and a retry window.
Fallback path
When TrustCaptcha returns a high bot score or the verification did not pass, you decide how to proceed. Make sure real users still have a way to finish:
- Users see a clear message (plain language) explaining what happened.
- The UI provides an accessible next step (e.g., email OTP / magic link).
- Users can retry without losing entered form data (where feasible).
- There is an escalation route (support/contact) for edge cases.
- The fallback path is keyboard- and screen reader-usable.
Documentation
- A short description of the verification approach (invisible, risk-based)
- Which routes are protected (login, signup, checkout, forms)
- Your step-up policy (what happens at elevated risk)
- The user-facing recovery path (OTP, support option, retry guidance)
Next steps
TrustCaptcha protects login, signup and checkout without a puzzle, which removes the accessibility problems that puzzle CAPTCHAs bring into these flows. Every plan comes with a 14-day free trial.
You can try TrustCaptcha for free if you want to test the mechanisms and accessibility for yourself.