TrustCaptcha and BITV accessibility
TrustCaptcha is a no-interaction invisible CAPTCHA that protects forms, logins and critical workflows from automated abuse. It avoids the classic accessibility problems of challenge-based CAPTCHAs: image puzzles, distorted text, time pressure and audio alternatives that often fail in practice. Under BITV, that means the bot protection is not the step where a keyboard or screen reader user gets stuck.
This page explains how TrustCaptcha fits into BITV-aligned accessibility expectations, what to consider when integrating it into user journeys, and how to document its impact for audits and accessibility statements.
What BITV compliance means in practice
BITV (in its current form BITV 2.0) is the German regulation on accessible information technology, most relevant to public-sector websites and mobile applications. In day-to-day engineering work, “BITV-ready” typically means:
- You design and test against recognized accessibility requirements (commonly EN 301 549 / WCAG-based success criteria).
- Core user journeys (authentication, forms, payments, service requests) work with keyboard-only navigation and assistive technologies.
- Errors are understandable, recoverable, and communicated programmatically.
- Third-party components do not introduce blockers, traps, or non-perceivable steps.
TrustCaptcha is a low-friction security control: it keeps those journeys accessible and still stops automated abuse.
Why traditional CAPTCHAs often fail accessibility
Challenge-based CAPTCHAs can conflict with accessibility requirements because they often:
- Rely on vision, hearing, or fine motor control
- Add unexpected focusable elements or third-party frames
- Create time pressure or complex instructions
- Increase cognitive load and comprehension demands
- Break established form patterns for screen readers and keyboard users
As an accessible CAPTCHA, TrustCaptcha avoids these patterns by removing the challenge step entirely.
How TrustCaptcha supports accessible user journeys
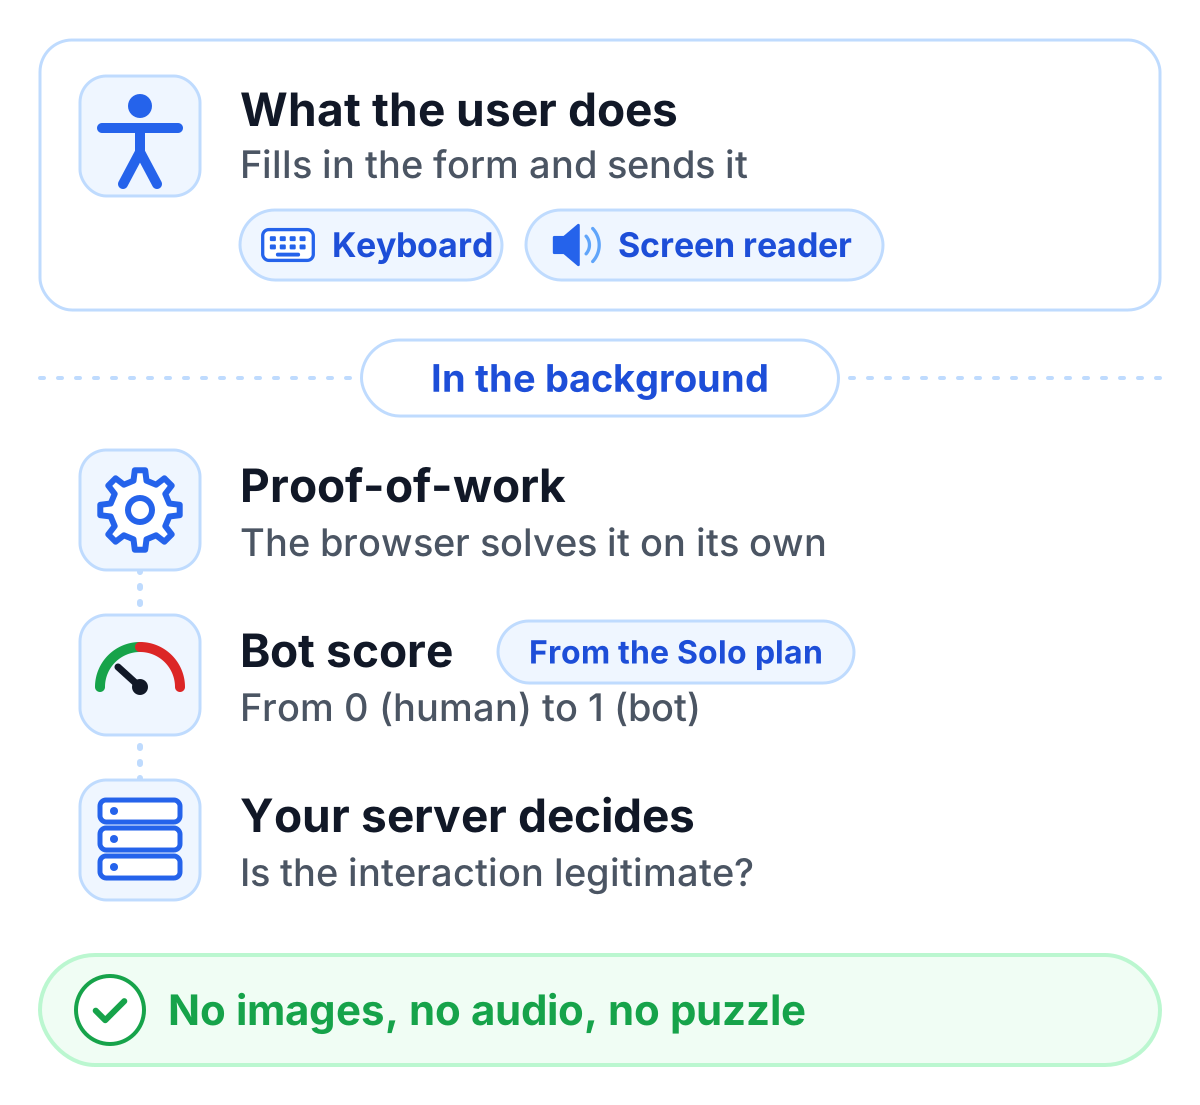
TrustCaptcha starts from a simple idea: bot protection should not turn into a test for the user. Instead of asking people to prove they are human, TrustCaptcha uses a proof-of-work mechanism that runs completely in the background and makes large-scale attacks expensive. From the Solo plan, it adds a bot score from 0 (very likely human) to 1 (very likely bot) that helps your server decide whether an interaction is legitimate.
Accessibility impact: mapped to WCAG principles
| WCAG principle | What to avoid | How TrustCaptcha helps |
|---|---|---|
| Perceivable | Visual/audio-only challenges | No challenge UI is presented to the user |
| Operable | Keyboard traps, extra focus stops | No complex interactive widget to navigate |
| Understandable | Complex instructions, puzzle solving | Standard form flow; errors can be explained plainly |
| Robust | Non-standard UI that breaks assistive tech | Keeps your form semantics intact |
Integration guidance for BITV-aligned deployments
Most of the accessibility work happens in the UI and in error handling. The recommendations below keep TrustCaptcha integrations predictable and usable for everyone.
1) Keep form semantics clean
- Use explicit
<label>elements and clear field instructions. - Ensure required fields and validation rules are communicated programmatically.
- Avoid placeholder-only labels.
2) Provide a human-friendly fallback path
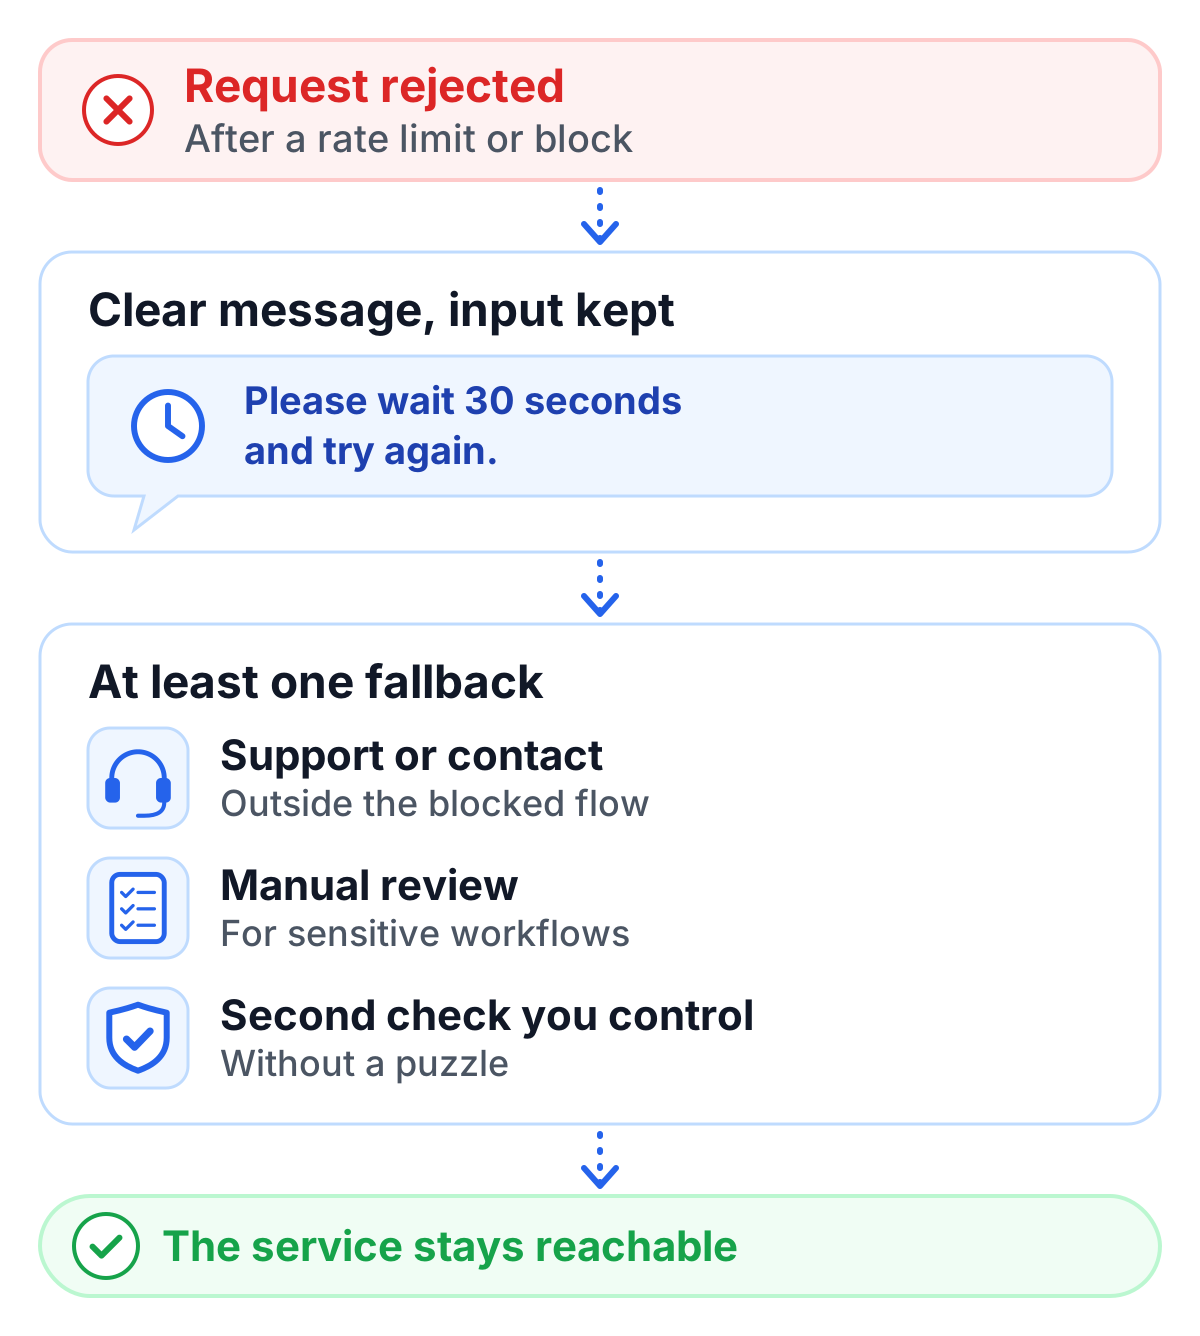
No security system is perfect, so a BITV-aligned design makes sure users are never stuck. Plan at least one fallback:
- A support/contact route that does not require the blocked flow
- Manual review for sensitive workflows
- A secondary verification method you control (without puzzles)
The goal is that people can still reach the service.
3) Avoid time pressure and confusing retry loops
If you rate-limit or block repeated attempts:
- Provide clear messaging (“Please wait 30 seconds and try again”)
- Avoid silent failures
- Let the user recover without losing form input where possible
Testing checklist
Use this checklist in QA and accessibility audits:
- Keyboard-only: complete the protected flow (Tab/Shift+Tab/Enter/Space)
- Screen reader: form labels, instructions, and errors are announced correctly
- Zoom and reflow: flow still works at 200% zoom and on mobile
- Error recovery: a rejected request provides a clear, reachable fallback path
- Documentation (if required): third-party component impact is recorded in your accessibility notes
Where to mention TrustCaptcha in accessibility documentation
If TrustCaptcha protects key user journeys (login, signup, checkout, service forms), you may want to reference it in:
- Your internal accessibility plan
- Your accessibility statement notes on third-party dependencies
- Your incident/exception process (how blocked users can get help)
Additional standards references
For additional materials and quick references, see:
- WCAG (Web Content Accessibility Guidelines)
- European Accessibility Act (EAA)
- EN 301 549 (ICT accessibility standard)
Next steps
If you want BITV-aligned accessibility without CAPTCHA friction, TrustCaptcha is built for that: bot protection without puzzles or user input. The widget starts on its own, and every plan comes with a 14-day free trial.
You can try TrustCaptcha for free if you want to test the accessibility and BITV compliance yourself.