How to prevent ecommerce fraud
Ecommerce fraud prevention starts with the bots, because most fraud at scale is automated. Put a bot check on login, signup, checkout and gift card forms and verify it on your server, then add payment checks, order monitoring and clear refund rules for the fraud that people commit by hand. The aim is not maximum friction. It is the right control at the right stage of the customer journey.
The measures at a glance:
- Block automation early with a CAPTCHA, rate limiting and API protection.
- Use adaptive authentication for login, password reset and high-risk actions, and multi-factor authentication for sensitive account actions.
- Secure checkout with payment checks such as tokenization, AVS, CVV and 3-D Secure, plus real-time transaction monitoring and anomaly detection.
- Review high-risk orders and suspicious behavior after the purchase.
- Protect promotions, referral programs and return flows from abuse, with clear refund and dispute rules.
- Train your teams and customers to recognize phishing and social engineering, and tighten controls during big promotions and seasonal peaks.
The CAPTCHA comes first because it sits at the very first point of contact. Set up correctly, it stops malicious automation before it turns into account takeover, card testing, spam, fake signups or inventory hoarding.
What is ecommerce fraud?
Ecommerce fraud is any unauthorized, deceptive or abusive activity against an online business, its customers or its systems, carried out for financial gain. Fraudsters go after user accounts, payment flows, promotions, refunds, gift cards, loyalty programs, forms, APIs and store policies. Many teams still think of fraud mainly as stolen credit cards, but it now runs through the entire customer journey, and ecommerce fraud prevention has to cover all of it.
That makes fraud an IT topic, not only a finance one. It touches application security, identity, bot management, customer trust and often compliance. Every store that lets people register, log in, check out, return goods or manage their own account has points where it can be abused. Fraudsters look for exactly the places where business logic, convenience for the user and weak controls meet.
Ecommerce fraud has also become harder to spot, because much of it looks like normal customer behavior. Attackers use real devices, leaked credentials, residential IP addresses, automated browsers and AI-assisted tools to blend into regular traffic. Rather than hammering a system in an obviously suspicious way, they imitate real customers at scale. Controls that only react after the fact are no longer enough.
Why ecommerce fraud is an IT risk
For IT and security teams, ecommerce fraud is a question of keeping the platform running and its data trustworthy. Direct losses from fraudulent orders, refunds, chargebacks and the extra work are only part of the cost. Fraud also drives up support costs, wastes infrastructure, distorts analytics, weakens marketing results and damages customer trust. In bad cases it can change how your payment provider rates your merchant account, lower your acceptance rates and strain your relationship with banks or payment processors.
The technical load is just as real. Fraud creates noisy traffic, inflates login attempts, raises API load and keeps your teams investigating incidents instead of improving systems. When bot-driven fraud hits at scale, security, engineering, fraud operations and customer support all feel it.
Ecommerce has no borders, which makes all of this harder. A fraudster can test stolen cards in one country, attack a merchant in another, use proxies from a third and cash out through accounts or marketplaces somewhere else. That works in the attacker’s favor. Defenders need controls that act in real time, at every touchpoint, before the abuse turns into a costly transaction or a compromised account.
Why ecommerce fraud keeps growing
Ecommerce fraud keeps growing because automation makes it cheap. A fraudster who once worked by hand can now use scripts, browser automation, credential lists, AI-written phishing and cheap servers to run millions of actions. The cost per attempt drops, while the volume and speed of the abuse go up.
The threat is also spreading in more directions. Fraud is no longer only about card-not-present payments. It includes account takeover, fake account creation, synthetic identities, gift card abuse, loyalty fraud, inventory hoarding, spam, promotion abuse, chargeback fraud and social engineering. Merchants rarely lose money to just one of these. They face several kinds of abuse at once, each hitting a different part of the stack.
Modern fraud also exploits business logic as much as technical weaknesses. A platform can be technically secure in a narrow sense and still be wide open to abuse of returns, discounts, referral rewards or self-service features. Ecommerce fraud prevention therefore has to combine security controls, transaction monitoring and defenses against automation.
Main types of ecommerce fraud
Good fraud prevention starts with knowing what the abuse looks like in practice. Tactics change all the time, but the main types of ecommerce fraud are well known by now.
| Fraud type | How it works | Common target areas | Business impact |
|---|---|---|---|
| Account takeover | Attackers use stolen credentials to get into legitimate accounts | Login, password reset, account settings | Fraudulent purchases, data theft, customers leaving |
| Bot-driven abuse | Automated systems carry out actions at scale | Login, signup, forms, inventory | Strained systems, fraud at scale, bad data |
| Card testing | Bots check whether stolen card details work, using low-value transactions | Checkout, donation forms, payment endpoints | Payment gateway abuse, fraud losses, fees |
| Gift card fraud | Stolen or guessed balances are redeemed or resold | Gift card portals, checkout | Lost margin, customer disputes |
| Payment fraud | Stolen cards or payment credentials are used for online purchases | Checkout, payment APIs | Direct losses, chargebacks, trouble with the payment processor |
| Friendly fraud | A customer disputes a legitimate purchase after receiving the goods or service | After the purchase, chargebacks | Lost revenue, support costs |
| Synthetic identity fraud | Fraudsters mix real and fake identity details to create believable accounts | Signup, financing, high-value orders | Late detection, long-term losses |
| Phishing and social engineering | Users or employees are tricked into revealing credentials or sensitive information | Email, support channels, fake landing pages | Stolen credentials, compromised accounts later on |
| Policy abuse | Loopholes in discounts, referrals, returns or loyalty programs are exploited | Promotions, refunds, referral flows | Shrinking margins, abused campaigns |
Each type hits a different stage of the customer journey, but many have one thing in common: bots make them bigger. Defenses against automation are therefore part of the basics of any serious ecommerce fraud strategy, not a niche extra.
Account takeover and credential abuse
Account takeover is one of the most damaging kinds of ecommerce fraud, because it gives attackers a legitimate customer account. Once inside, they change addresses, redeem loyalty points, place orders, pull out saved payment details or collect personal data. Because the activity comes from a real account, it can look perfectly normal. Our page on account takeover protection covers the defenses in detail.
Most account takeover campaigns start with credential stuffing. Attackers take username and password pairs from old data breaches and test them in bulk against store login pages, counting on people who reuse their passwords. Even if only a small share of the pairs work, the volume makes it pay off.
Strong password rules and rate limits help, but they do not solve the problem. Credential stuffing is distributed, automated and persistent. This is where a CAPTCHA fits: it interrupts bot traffic before any credentials are checked, so fewer accounts get compromised and your login systems are spared mass abuse.
Payment fraud, card testing and checkout abuse
Payment fraud is what most people think of first when ecommerce fraud comes up, and with reason. Card-not-present transactions are an easy target, because the attacker never needs to hold the card. But payment fraud is no longer just about placing fraudulent orders.
One especially costly variant is card testing, also called a carding attack. Bots check stolen card numbers through small payments or authorization attempts, and the merchant becomes an unwilling test environment. That can mean transaction fees, closer scrutiny from your payment provider and a lot of disruption. If nobody stops it early, the same setup is then used for larger fraudulent purchases.
Checkout can be abused beyond the card details, too. Attackers exploit guest checkout, address changes, shipping tricks and gift card redemption. Because checkout has to stay quick for real customers, it is a favorite target for automation.
A CAPTCHA is useful at this stage because it tells real shoppers from scripted payment attempts. Not every CAPTCHA does that well, though. One that only adds a puzzle or a short delay does little against modern automated payment abuse. Stopping card testing and checkout automation takes real bot detection and a way to make each attempt cost the attacker more.
Friendly fraud, policy abuse and hidden revenue loss
Not all ecommerce fraud looks like a cyberattack. Friendly fraud happens when a customer disputes a legitimate charge, either on purpose or because they do not recognize it. For the merchant the result is the same: lost revenue, extra support work and the risk of chargebacks.
Policy abuse gets less attention than it deserves. Fraudsters and opportunists exploit return rules, referral programs, loyalty points, free trials, discount codes and promotions. No stolen card or password has to be involved, and it still costs real money.
IT and fraud teams should keep an eye on both, because bots often help here as well. Automated signups farm discounts. Scripts test coupon logic or create fake referrals in bulk. So automation is not only a problem at login and payment. It also undermines your business logic and your pricing.
Why ecommerce fraud detection is so difficult
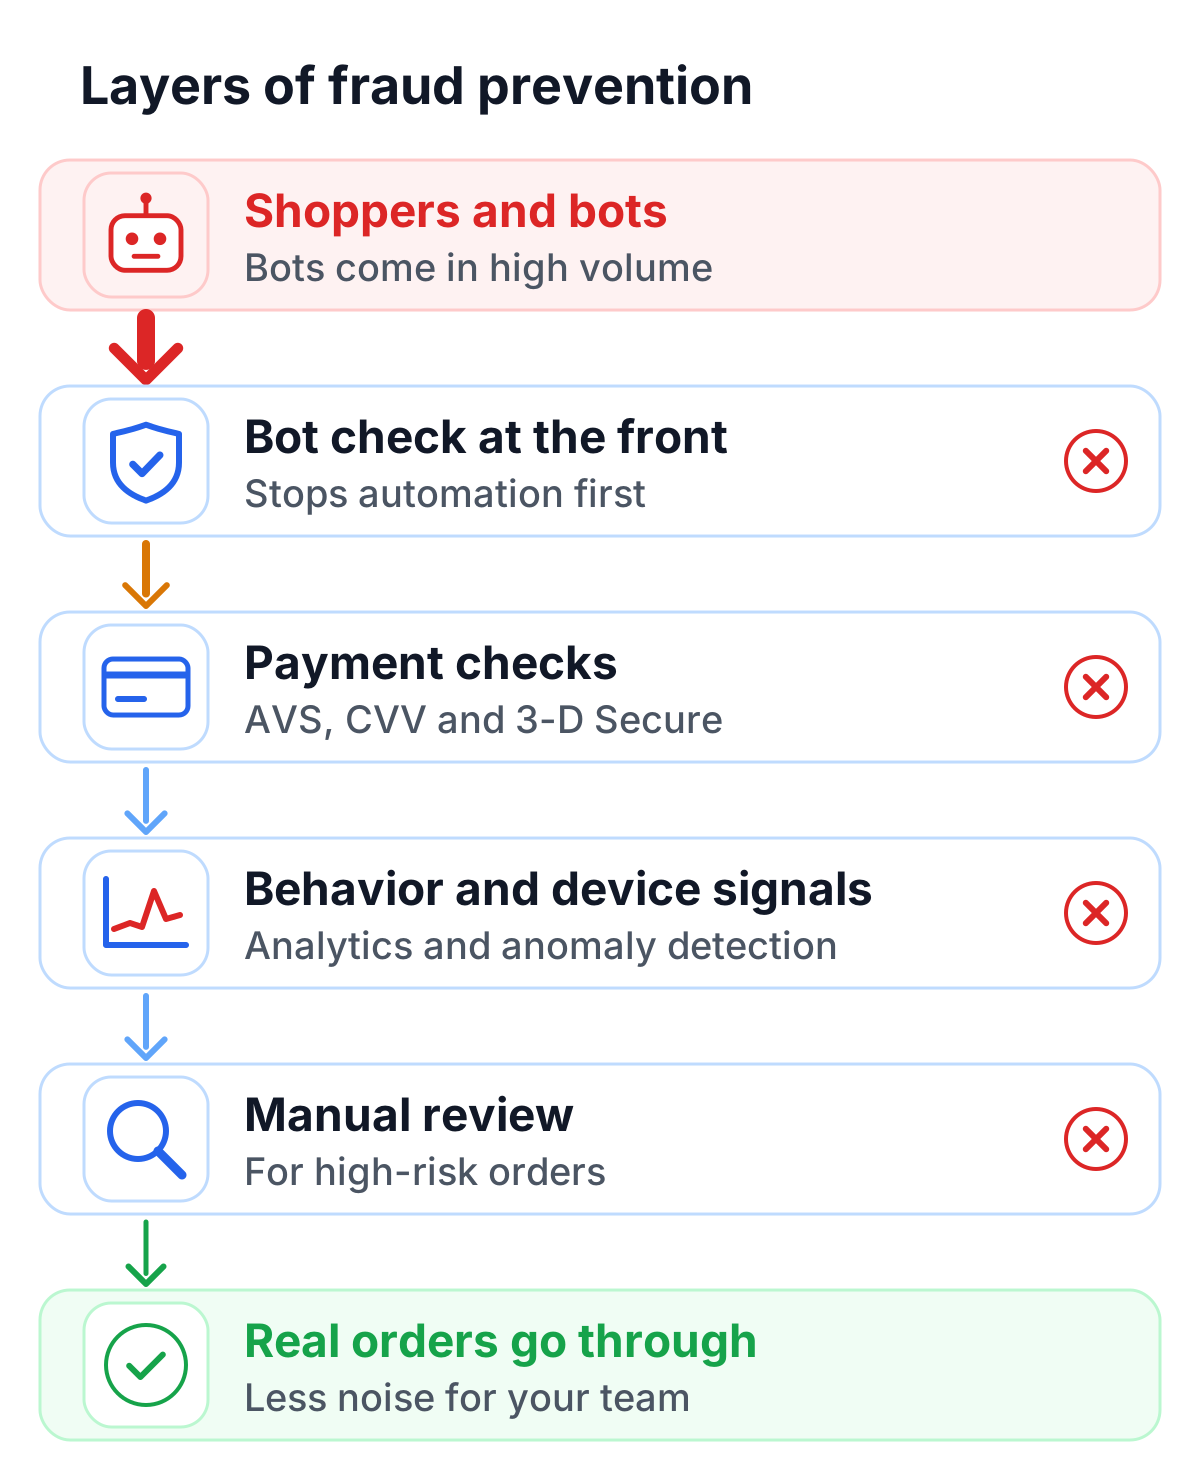
Ecommerce fraud is hard to detect because legitimate and fraudulent behavior often look alike. A login from a new device can be harmless or hostile. A large order can come from a loyal customer or from a compromised account. A sudden burst of form traffic can be a successful campaign or a bot attack. Rule-based systems alone struggle in these gray areas.
Fraudsters also adapt quickly. Once they figure out what triggers a static rule, they rotate IP addresses, change their traffic patterns, use more realistic browsers and spread their attacks over time. Relying on any single control on its own is risky.
Fraud prevention therefore has to be layered and able to adapt. Payment checks such as AVS, CVV and 3-D Secure are still useful. Behavioral analytics, anomaly detection and device signals add depth. Manual review still has a place for high-risk orders. But one lesson comes up again and again: if bots can reach your systems unhindered, they put pressure on every control further down the line.
Why a CAPTCHA belongs at the front line
A CAPTCHA is still one of the most practical tools against automated abuse in ecommerce, and for many shops it is the default anti-bot control. Its job is simple: decide whether a request probably comes from a human or from a machine. That sounds basic, but it matters, because so much of today’s fraud depends on machines.
Many high-volume attacks only pay off with automation. Credential stuffing works at scale only when bots can test huge numbers of logins. Card testing depends on repeated payment attempts. Fake account creation needs automation to produce many accounts cheaply. Inventory hoarding relies on bots reaching limited products faster than people. A CAPTCHA breaks that loop on login pages, signup forms, checkout, password reset pages, gift card lookups, API endpoints and support forms at once. Few controls in an ecommerce stack cover that much ground for the effort.
Not every CAPTCHA does this well, though, and what makes a good CAPTCHA here is detection, not friction. Traditional CAPTCHAs rely on image puzzles, challenge-response tasks or interaction tests that put the work on the user. They add friction to the flows where conversion matters most, cause accessibility problems and annoy real customers at login and checkout. And they often act more like speed bumps than detection systems: they may slow bots down, but they tell a business little about whether a session is automated. Attackers can script around a hurdle like that, spread the load or simply accept the delay as a cost of doing business.
Two things make the difference. Proof-of-work raises the cost of scale: fraud operations are profitable when each automated attempt costs almost nothing, and proof-of-work makes the attempts expensive in aggregate, which hits high-volume attacks such as credential stuffing, fake account creation and card testing hardest. A bot score gives an explicit signal about how likely a request is automated. That is worth more than a delay, because your team can respond with more precision: block, challenge, monitor or escalate.
How TrustCaptcha protects ecommerce workflows
TrustCaptcha combines both. Instead of relying on visible puzzles, it pairs proof-of-work with bot scoring (from the Solo plan), which both deters bots and detects them. A small computational task costs a real customer a moment. Multiplied across thousands of automated requests, it becomes expensive for whoever runs the bots. The bot score then tells your server how likely each request is automated, so you do not have to treat every request the same way.
Ecommerce fraud does not happen in one place. It shows up at many high-risk touchpoints, and each of them benefits from bot protection.
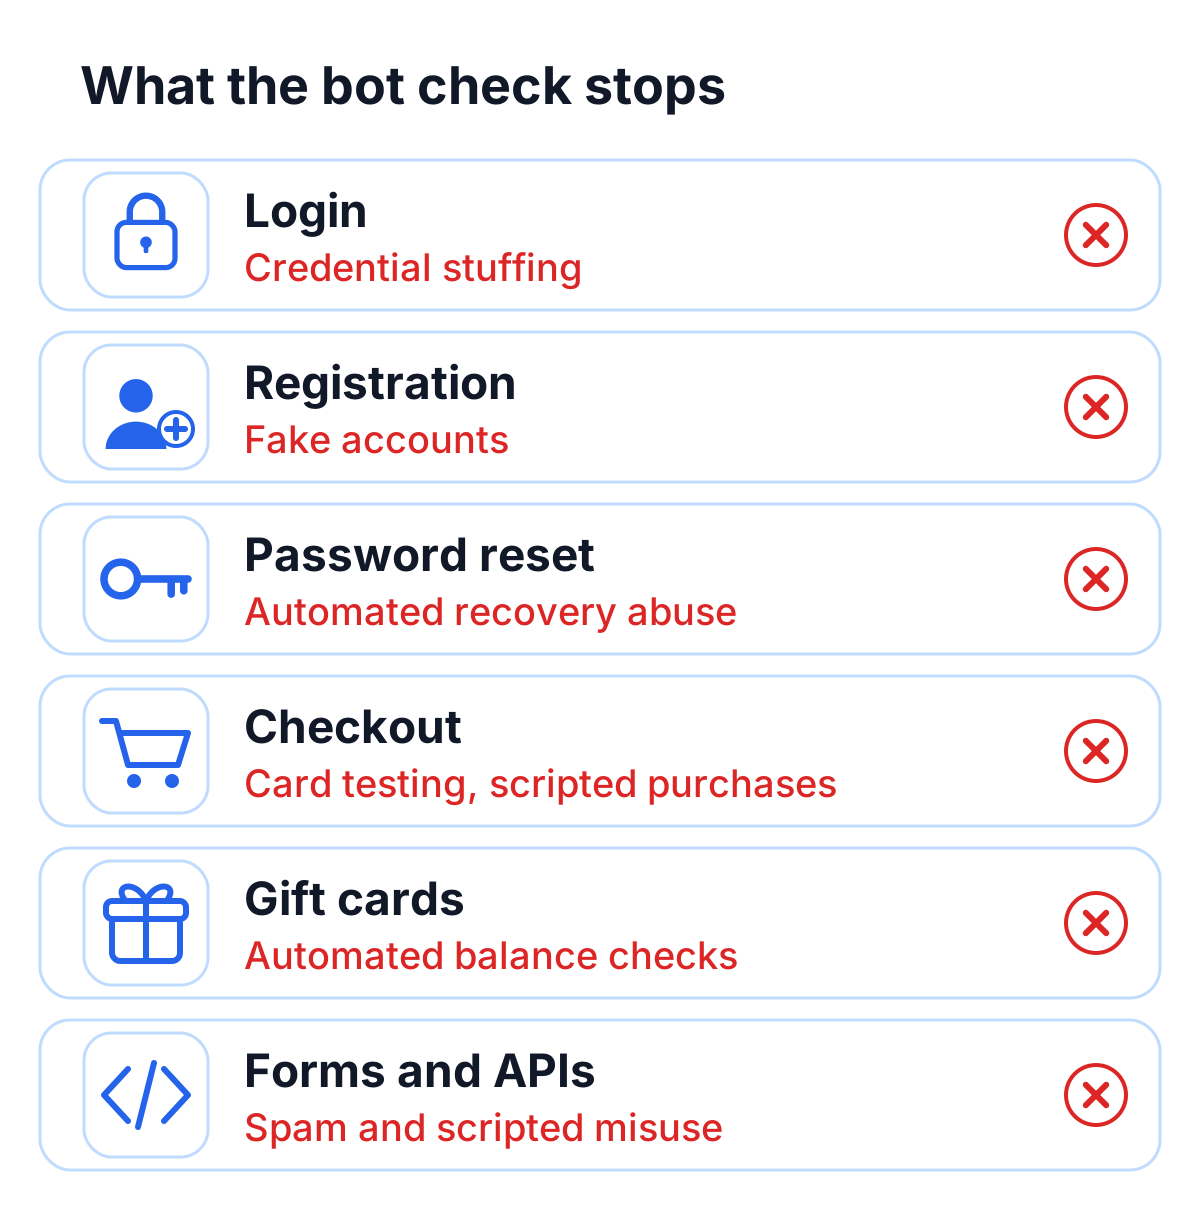
On login pages, TrustCaptcha stops credential stuffing before bots can abuse your authentication at scale. On registration pages, it cuts down fake account creation that feeds promotion abuse, spam and identity fraud. On password reset flows, it prevents automated abuse of account recovery. On checkout pages, it blocks card testing and scripted purchases. On gift card portals, it stops automated balance checks and redemption abuse. On forms and APIs, it cuts down spam, scripted misuse and bots scouting your systems; our page on form spam protection covers the contact form side.
The broader benefit is that TrustCaptcha works early. Instead of expecting downstream systems to catch every malicious action once it is inside the workflow, it reduces the number of abusive requests those systems ever see.
TrustCaptcha is also privacy friendly: it sets no cookies, processes data in EU data centers and comes with a Data Processing Agreement for every customer. For businesses in privacy-conscious markets or regulated sectors, that matters. Protection and responsible data handling should not be a trade-off, and with TrustCaptcha, bot protection works without invasive tracking.
Best practices for deploying TrustCaptcha
TrustCaptcha works best when you place it deliberately along the customer journey rather than on a single page. In most stores, the top priorities are login, signup, password reset, checkout, payment APIs, gift card features and high-value forms.
It also belongs inside a broader security setup. A CAPTCHA does not replace transaction monitoring, fraud models or payment checks. It makes them more effective by cutting the amount of bot-driven abuse they have to handle, which means cleaner signals, less noise for your team and less wasted infrastructure.
For anyone buying security tools, this combination is the point: TrustCaptcha strengthens fraud prevention while keeping usability and privacy intact. Security teams are no longer judged only on the threats they block. They are also expected to protect performance, accessibility, conversion and compliance.
Try TrustCaptcha
Ecommerce fraud now touches every stage of online retail, from account creation through checkout to what happens after the purchase, and bots make most of it bigger. Start with the login and checkout forms, where bots do the most damage.
Every plan starts with a 14-day free trial, and non-commercial websites can use TrustCaptcha for free. Start your free trial and see how it reduces ecommerce fraud without adding friction for your customers.