How to stop spambots on contact forms
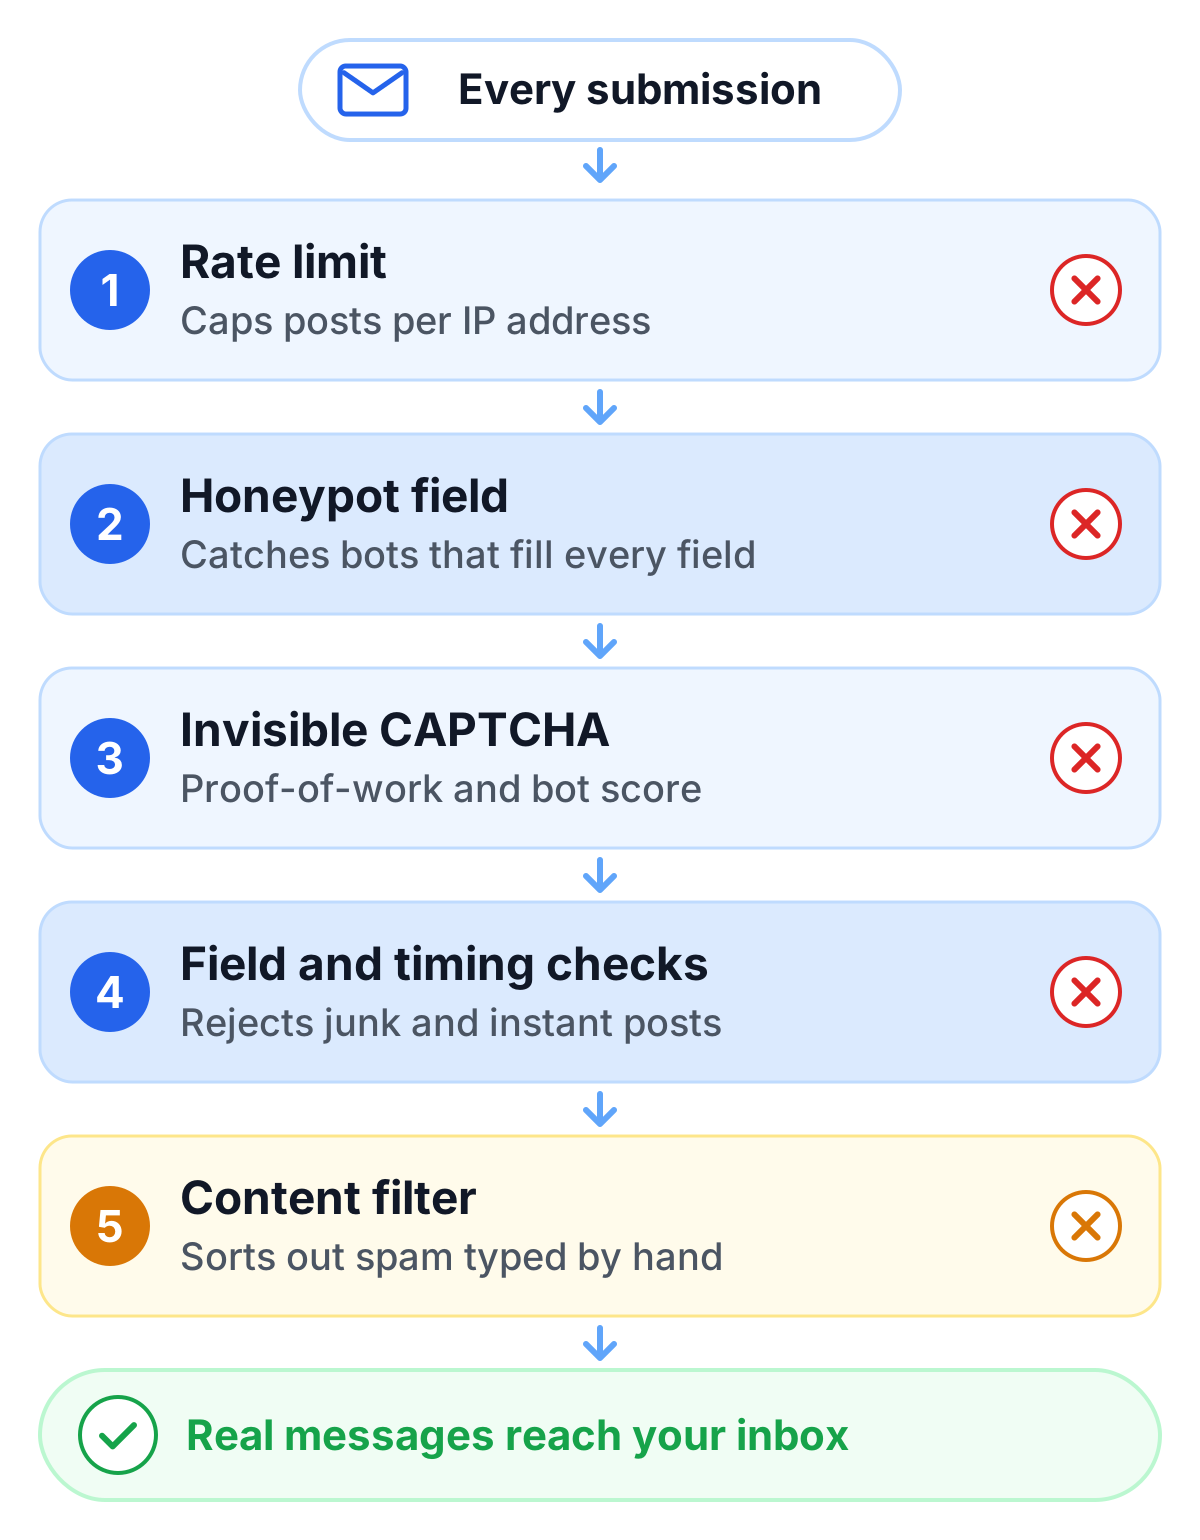
Check every submission on your server, because a spambot can skip anything that runs only in the browser. Give each post a few checks the visitor never sees: a hidden honeypot field, a rate limit per IP address, and an invisible CAPTCHA that makes each post cost computing time and scores how automated it looks. On a typical contact form that makes bot spam rare without a single puzzle, and what still gets through is mostly spam that people type by hand.
| Layer | What it stops | What gets past it |
|---|---|---|
| Honeypot field | Bots that fill in every field they find | Bots that render the page or were written for your form |
| Rate limit | Floods from one IP address | Bots spread over many IP addresses |
| Invisible CAPTCHA | Bots at volume and automated browsers | A person typing spam by hand |
| Field and timing checks | Links in the name field, broken email addresses, forms sent the moment the page loads | Spam that is well formed and patient |
| Content filter or moderation | Sales pitches and link spam typed by hand | Some real messages, if the filter is strict |
Good form spam protection is a stack of these layers, because none of them is enough alone and none of them is expensive. The rest of this page explains where form spam comes from and how to set up each layer.
Where form spam comes from
Most spam that reaches a contact form is sent by bots, and the people who run them have no interest in your site in particular. They want any open form that delivers a message to a human, ideally with a link in it.
Bots that post the form directly
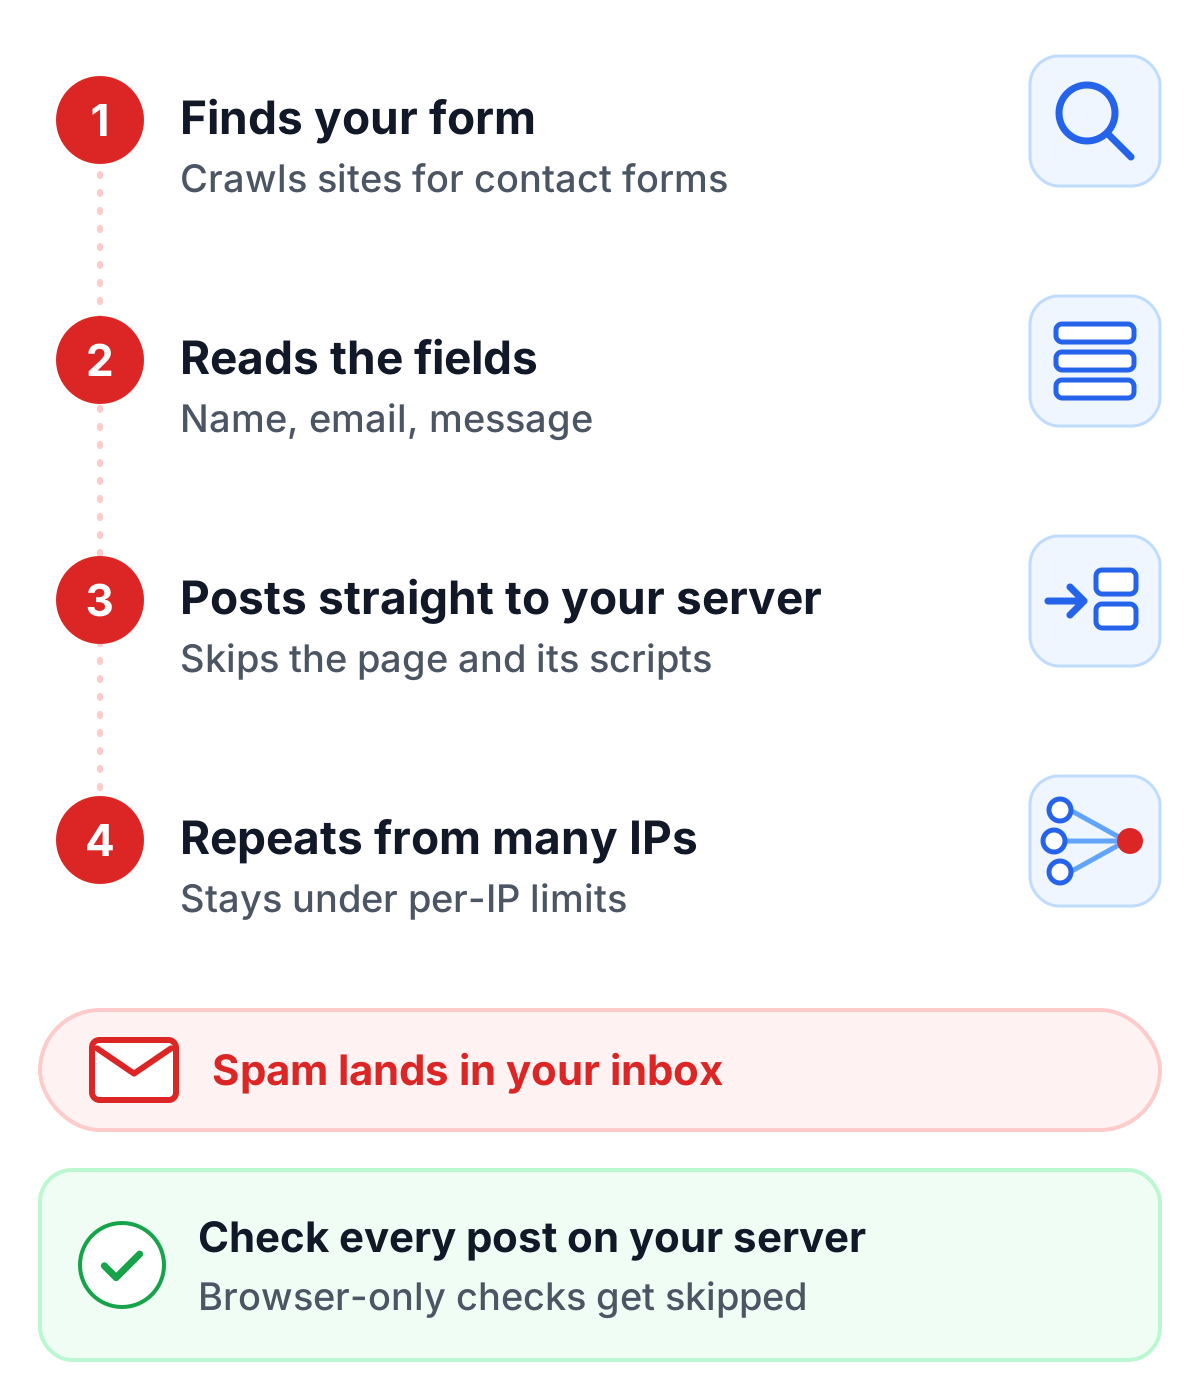
The cheapest spambot never opens your page in a browser. It reads the HTML once, notes the field names and the address the form sends to, and from then on posts straight to that address as often as it can. Because it skips the page, it also skips every script on it. A check that only runs in the browser, such as JavaScript that validates the email field, simply never runs.
Bots that run a real browser
The next level loads the page in a headless browser, runs its scripts and fills in the visible fields the way a visitor would. These bots get past many simple tricks, including most honeypot fields, because they see the page as a person does. They are slower and cost more to run, and that cost is what proof-of-work raises.
Spam typed by people
Some form spam is typed by hand: link builders, “free SEO audit” offers, people paid per submission. No bot check stops a person, and no honest CAPTCHA vendor claims otherwise. This part needs a content filter or someone who reads the inbox.
Why form spam costs more than inbox space
A contact inbox full of spam is annoying. The less visible costs are worse. Real inquiries drown between fake ones, and whoever answers them learns to skim, which is when a real customer gets missed. Spam that flows on into your CRM or newsletter list corrupts the data the sales team works with, and the links in it reach exactly the person whose job is to open messages from strangers.
Watch your confirmation emails as well. If the form sends the visitor a copy of their message, a bot can put someone else’s address in the email field and its spam in the message, and your mail server delivers that spam under your domain. Enough complaints and your own emails start landing in spam folders. Leave the message text out of confirmation emails, and send them only once a submission has passed your checks.
Spam protection for forms, layer by layer
Good spam protection for forms is built from cheap checks. Each layer below runs on your server, roughly in the order shown here.
Rate limits
A rate limit caps how many submissions one IP address can send in a given time. A contact form rarely needs more than a few an hour from the same address, so the limit can be tight without anyone noticing. Most web servers and frameworks have one built in.
Two things to keep in mind. Bots that rotate through many IP addresses, which residential proxy networks make cheap, stay under any per-IP limit. And whole offices and mobile networks often share one address, so a limit that is too tight blocks real people instead.
Honeypot field
A honeypot is an extra field that you hide from people with CSS. A bot that fills in every field fills in this one too, and your server drops the submission. It costs nothing and catches a surprising share of the spam from bots that post directly. Our article on the honeypot CAPTCHA covers the setup in detail.
Hide the field from assistive technology as well (aria-hidden="true" and tabindex="-1") and switch off autofill for it (autocomplete="off"). Otherwise a screen reader user or the browser’s autofill may fill it in, and a real message disappears without anyone knowing. Bots that render the page and check what is visible skip the field.
Invisible CAPTCHA: proof-of-work and bot score
This is the layer for bots that behave like visitors. An invisible CAPTCHA runs in the background while the visitor fills in the form. With proof-of-work, the browser solves a small computational task before the form goes out: a moment for one visitor, real hardware and time for a bot that wants to send a hundred thousand posts. A bot score rates how automated the request looks, from signals such as the browser and how the page was used. Our guide to the bot score explains how to read one.
The CAPTCHA hands the browser a token, and your server has to check that token with the provider before it accepts the submission. Skip that step and a bot that posts directly walks straight past the CAPTCHA, because it never loads the widget.
Field and timing checks
Your server knows things about a submission that bots often get wrong. A URL in the name field, an email address whose domain does not exist, a message that is nothing but links. A form sent one second after the page loaded was not filled in by a person. Rejecting these takes a few lines of code. Keep the rules loose enough that a customer with an unusual name or a short message still gets through.
Content filters and moderation
What is left is mostly spam typed by people, plus the occasional well-built bot. A content filter scores the text of each message against known spam. Language models have made this layer weaker: a sales pitch written by one reads like a real inquiry, and keyword lists miss it. Use the filter to sort suspicious messages into a separate folder, not to delete them.
Stop form spam without a puzzle
Image grids and distorted letters are the oldest spam protection for forms, and on a contact form they are a bad trade. The person who wants to send you a message is the person you want to hear from, and every extra step is a reason to leave. Puzzles also shut out visitors who cannot see or hear the challenge, and they no longer stop bots reliably, because image recognition and paid solving services get through most of them.
You can stop the simple spambots without any CAPTCHA at all: a honeypot, a rate limit and field checks handle them. Once bots run a real browser, you need proof-of-work or a bot score, which is what an invisible CAPTCHA adds without showing anything to solve. Our overview of CAPTCHA alternatives compares the methods that replace the puzzle and where each one fails.
Contact form spam on WordPress
WordPress sites get more form spam than most, because bots know where to look: the same form plugins with the same field names on a huge number of sites. The TrustCaptcha WordPress CAPTCHA plugin works with Contact Form 7, Elementor Forms, WPForms, Gravity Forms, Ninja Forms, Fluent Forms and Forminator, and also protects comments, login, registration and the WooCommerce checkout. The plugin checks the result on your server, so a bot that posts straight to the form gets rejected as well. For the most common setup there is a step-by-step guide: Contact Form 7 CAPTCHA.
Signup forms attract a different kind of bot, one that creates accounts instead of sending messages. Our guide on how to prevent fake account creation covers that case.
Where TrustCaptcha fits
TrustCaptcha is the invisible CAPTCHA in this stack, and it brings a honeypot of its own. Every plan includes dynamic proof-of-work, which gets harder as the risk of a request rises, so a bot flood becomes expensive. Every widget also contains several hidden honeypot fields that need no setup. From the Solo plan, bot detection scores each request from about 35 signals, and you can add your own proof-of-work rules and IP allowlists and blocklists. Visitors see a small widget that checks itself; there is nothing to click or solve. If you want no visible widget at all, the Captcha Branding add-on removes it.
Your server validates the result with one API call. By default it can fetch each result only once, so a bot cannot reuse one solved token for a batch of posts. TrustCaptcha sets no cookies, processes data in EU data centers and comes with a Data Processing Agreement for every customer. Rate limits, field checks and the occasional look at the inbox stay with you, and they work well alongside it.
Try TrustCaptcha
Every plan starts with a 14-day free trial, and non-commercial websites can use TrustCaptcha for free with 500 verifications a month. Start your free trial and put it on your contact form first, since that is usually where the spam shows up.