What is a social engineering attack?
A social engineering attack is a method where attackers exploit human weaknesses to gain access to sensitive information or protected systems. Instead of breaking into computers or networks technically, the attacker relies on psychological manipulation. The goal is to prompt the victim to take certain actions, such as revealing passwords, downloading malware, or granting access to secured areas. Social engineering targets natural human reactions like trust, fear, curiosity, or helpfulness and is therefore often referred to as “human hacking.”
What makes social engineering attacks dangerous is that they are hard to spot. Firewalls and antivirus software often do not help, because these attacks rely on human interaction. Companies are particularly at risk because they often have numerous employees with access rights and sensitive data. A single mistake can have severe consequences, such as the loss of confidential information, financial damages, or reputational harm.
How social engineering attacks work
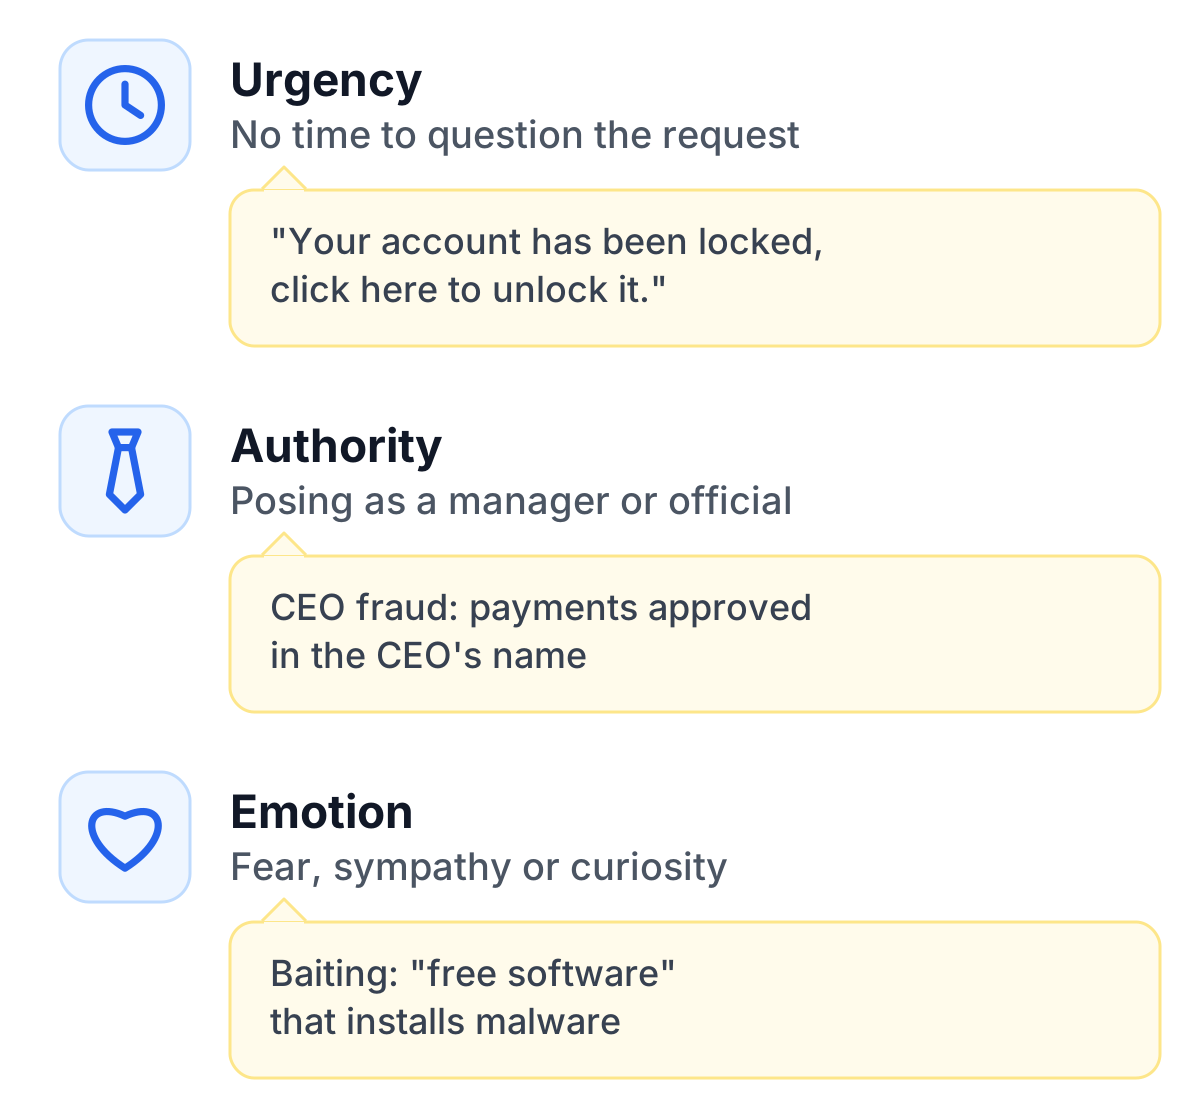
Social engineering works through psychological tricks that win the victim’s trust or catch them off guard. They often try to create a situation where the victim does not have time to question the request. The most common techniques are based on three principles:
- Creating urgency: Attackers pressure the victim with messages such as “Your account has been locked, click here to unlock it.” Under stress, people often act without thinking and fail to question such requests.
- Impersonating authority: Attackers pose as authoritative figures, such as managers or officials, to compel the victim to take action. A typical tactic is the so-called CEO fraud, where perpetrators pretend to act on behalf of a CEO to authorize financial transactions.
- Emotional manipulation: People are strongly influenced by emotions like fear, sympathy, or curiosity. For instance, in baiting, the victim is enticed by an attractive offer like “free software” and ends up downloading malware.
These psychological methods make social engineering one of the most effective forms of attack. Even trained individuals can be deceived in stressful situations or by well-thought-out deceptions.
Examples and impacts
Social engineering attacks can occur in various scenarios and are not limited to digital communication. A classic example is a phishing attack, where the victim receives an email with a fraudulent message claiming to be from a trusted source. The email prompts the victim to provide sensitive information or click on a malicious link. These attacks are widespread because they are easy to execute and often very effective.
Another example is pretexting, where the attacker pretends to be someone with a plausible reason to request information. For instance, an attacker might pose as IT support, claiming to resolve technical issues and requesting login credentials. The credibility of such scenarios is often enhanced by small details, such as mentioning the victim’s name or position.
The consequences of such attacks can be severe. In companies, a successful attack can result in the theft of confidential customer data, disruption of systems, or significant financial losses. In one well-known case from 2019, an energy company lost €220,000 through a manipulated call. The attacker used an AI-generated voice resembling the CEO to convince the accounting department to make a transfer.
Protecting against social engineering
Technology alone does not stop social engineering attacks. Awareness and training matter most. Employees should be regularly educated about the dangers and trained to recognize suspicious activities. This applies to email communication as well as phone calls or personal interactions.
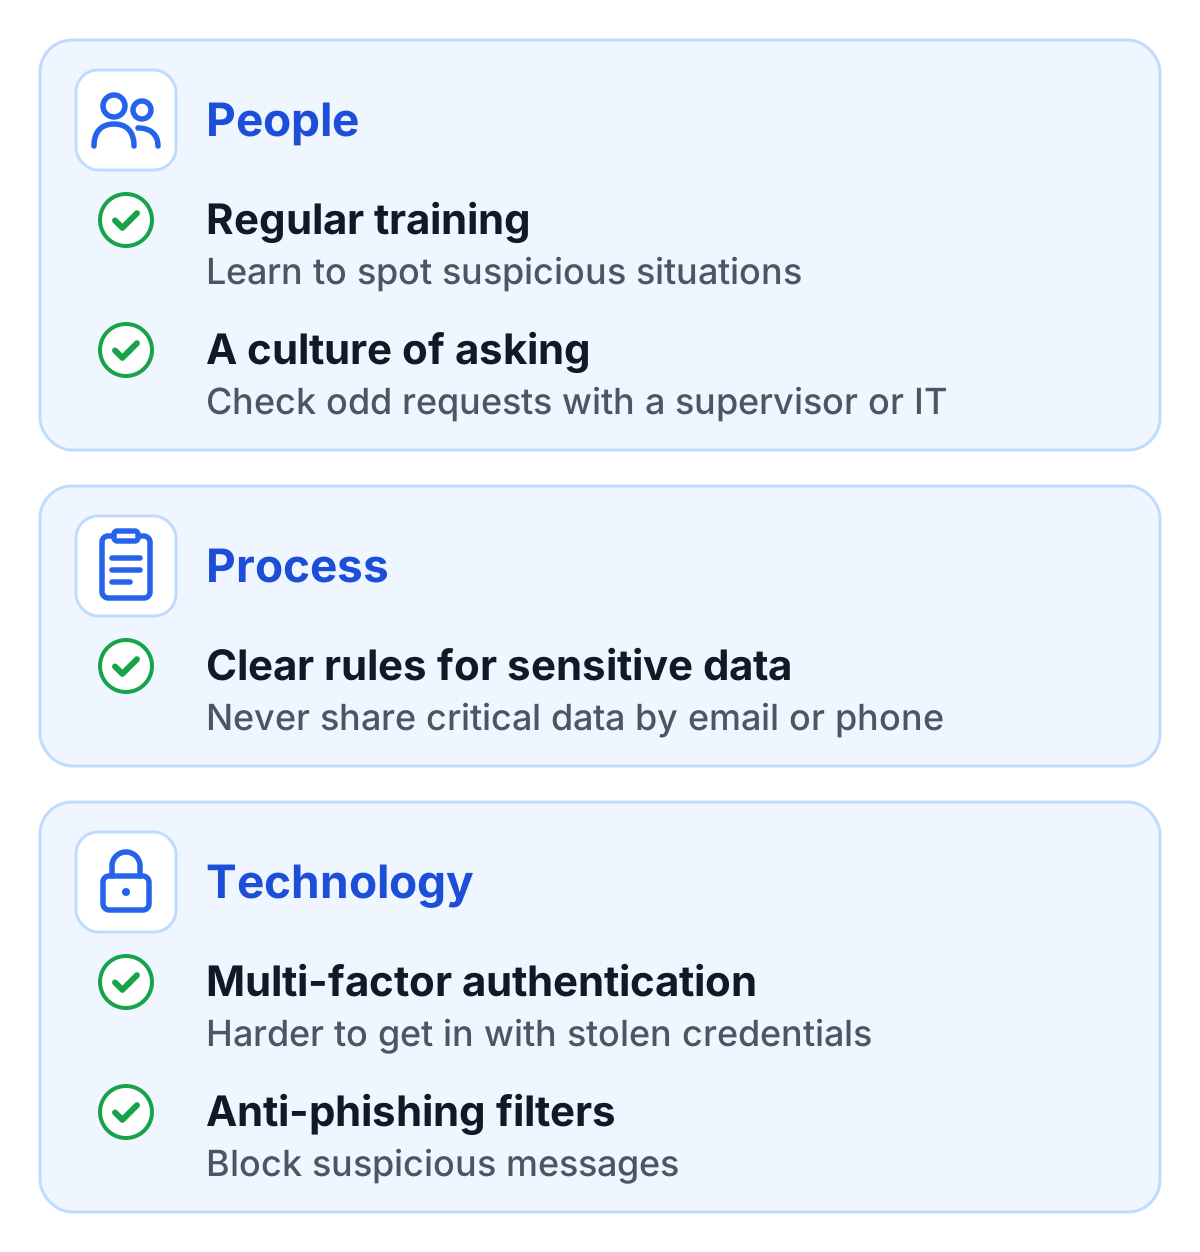
Technical measures still reduce the risk. Multi-factor authentication and account takeover protection make it harder for attackers to access systems, even if they obtain login credentials. Anti-phishing filters in email programs can automatically block suspicious messages. Additionally, companies should establish clear guidelines for handling sensitive information, such as never sharing critical data via email or phone.
Just as important is a company culture in which questioning unusual requests is normal. Employees should feel confident reaching out to supervisors or IT departments if they have doubts about a request. Attackers often rely on victims feeling uncomfortable asking questions or feeling obligated to follow instructions.
Conclusion
Social engineering attacks are one of the biggest challenges in cybersecurity because they target human nature directly. They bypass technical safeguards and use psychological tricks to deceive victims. The range of attacks includes emails, phone calls, and direct personal interactions.
The best defense combines vigilance, training and technical measures. Employees need to recognize suspicious situations and know how to respond, and companies need clear security policies and processes behind them. Culture counts as much as technology: in a team where asking “is this request real?” is normal, attackers have a much harder time.
No team is immune. But regular awareness work and a few firm rules, such as confirming payment requests through a second channel, lower the risk considerably for companies and individuals alike.