

Introduction
Many cyberattacks use known weaknesses that an update would have closed. Zero-day exploits are different and much harder to fight: attackers use a vulnerability before anyone has discovered or patched it. That makes them a serious problem for companies, governments and individuals, because traditional security tools often cannot detect them. That makes it all the more important to know what zero-day exploits are, why they are so dangerous and what you can do to reduce the risk.
What is a zero-day exploit?
A zero-day exploit is an attack on a vulnerability in software, hardware or firmware that the vendor or developer does not know about yet. Hackers use it before a patch exists, so there is nothing to install that would stop them. “Zero-day” means the manufacturer has had zero days to fix the flaw.
How do zero-day vulnerabilities arise?
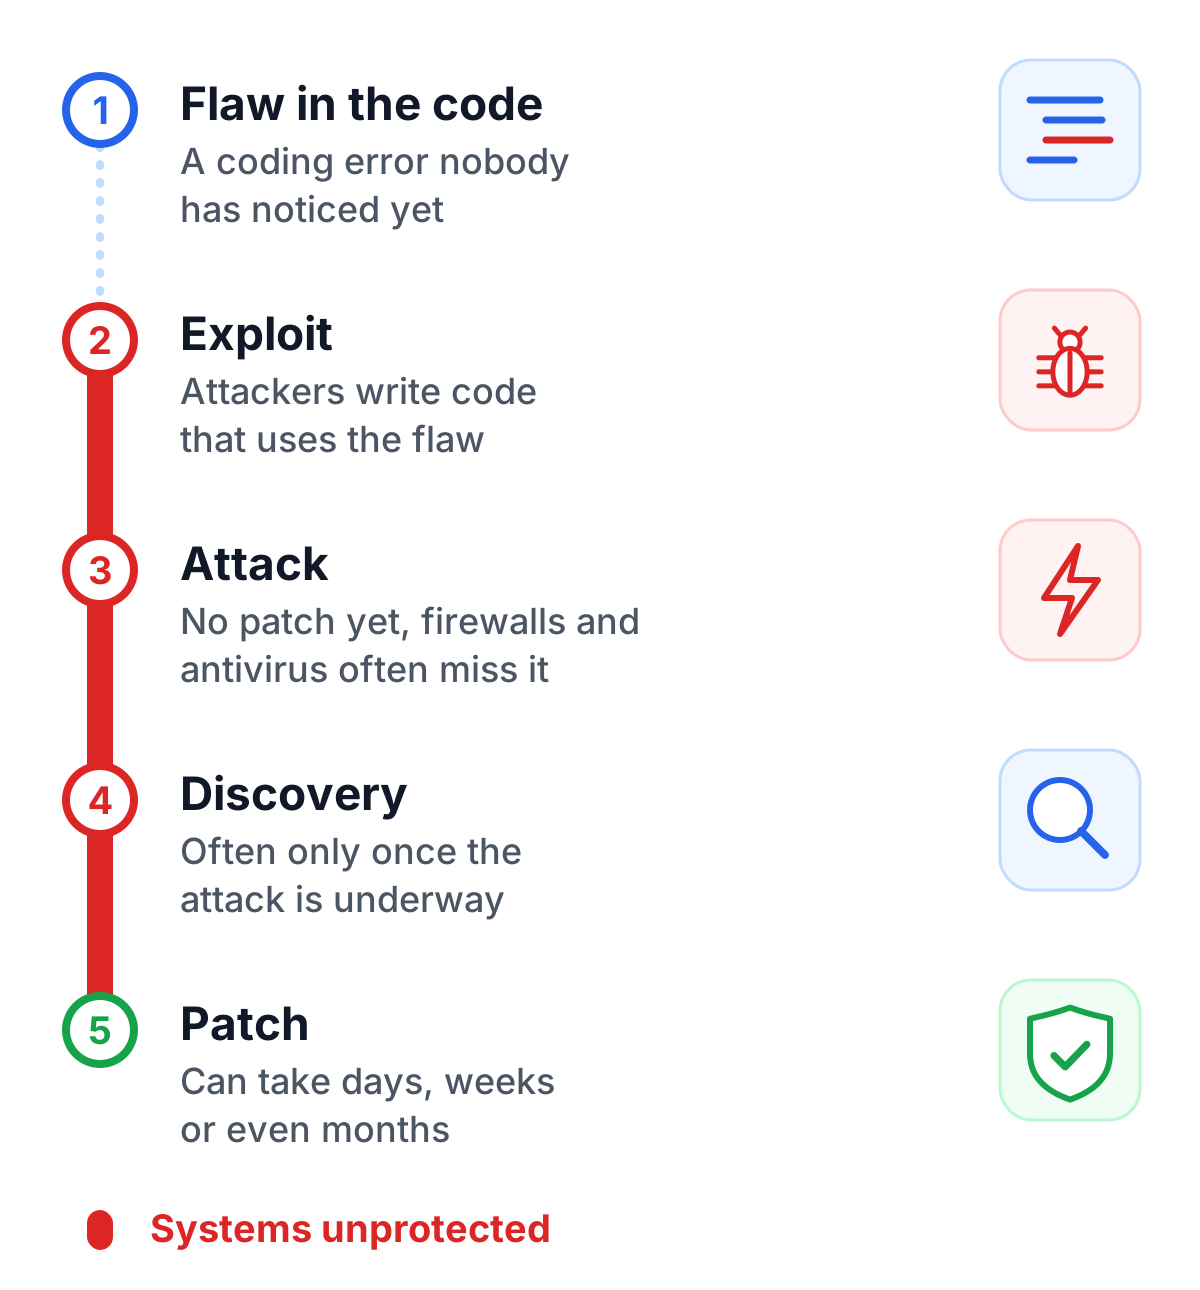
Most zero-day vulnerabilities start as coding errors that nobody noticed during development. Complex systems and tight schedules make such errors more likely. Testing is often part of the problem too: teams check whether features work and how fast they are, and spend less time on security.
On top of that, modern IT systems keep getting more complex, which makes them harder to secure. Software today is often composed of open-source libraries and third-party components. Each of these components can harbor vulnerabilities that attackers may exploit.
Differences between vulnerabilities and exploits
A zero-day vulnerability and a zero-day exploit are not the same thing. The vulnerability is the security flaw that could in theory be exploited. An exploit, on the other hand, is the specific code or method used to take advantage of the vulnerability. A vulnerability only becomes an immediate threat through an exploit.
Why are zero-day exploits so dangerous?
The danger of zero-day exploits lies primarily in their invisibility and the speed with which they are exploited. Because such vulnerabilities are still unknown, traditional security tools such as firewalls or antivirus software often miss them. Systems stay exposed until an update or patch is available, and that can take days, weeks or even months.
Invisibility and unpredictable damage
Companies often learn about a vulnerability only when an attack is already underway. By then the damage may be done: lost data, disrupted operations, a damaged reputation and sometimes legal consequences.
Targeted attacks
Zero-day exploits are often used in highly targeted attacks involving industrial espionage, cybercrime, or state-sponsored cyberattacks. A prominent example is the Stuxnet worm, specifically developed to sabotage industrial control systems in Iran. Such attacks are precise and often very difficult to detect because they are tailored to the target environment.
Examples of zero-day exploits
Three well-known attacks show how far the damage from an exploit can reach, and why patching quickly matters:
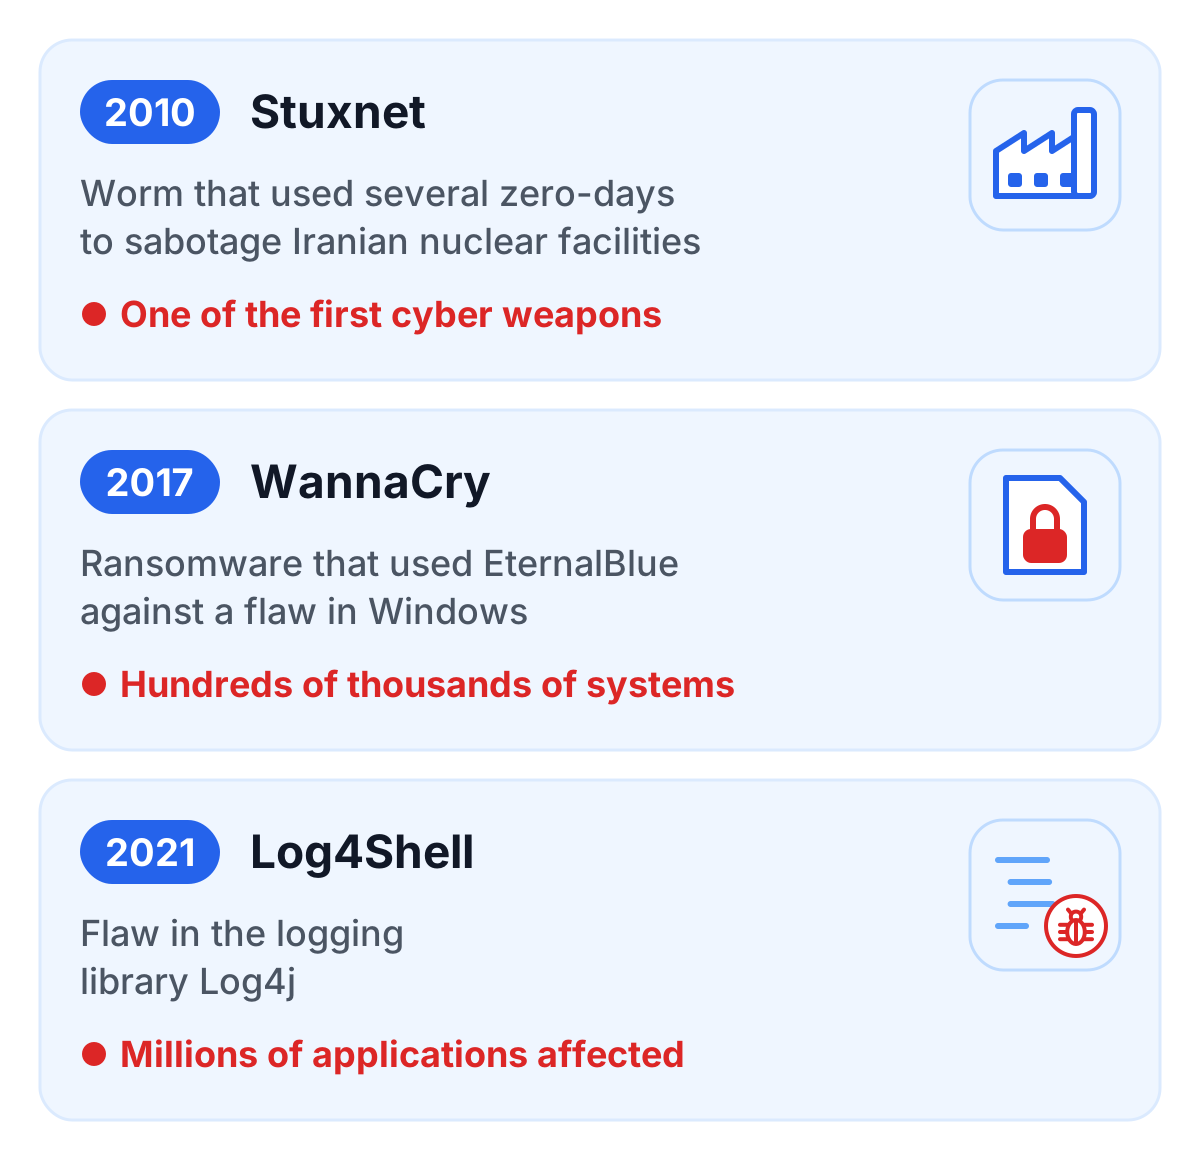
- Stuxnet (2010): This worm is considered one of the first cyber weapons ever. It exploited several zero-day vulnerabilities to sabotage Iranian nuclear facilities and showed that a cyberattack can physically damage critical infrastructure.
- WannaCry (2017): This ransomware used the EternalBlue exploit against a vulnerability in Microsoft Windows. EternalBlue had started out as a zero-day, but Microsoft had released a patch two months before the attack. Within a few days, WannaCry infected hundreds of thousands of systems that had not installed it, causing damage estimated in the billions of dollars.
- Log4Shell (2021): A vulnerability in the logging library Log4j became public in 2021 and set off a global security scramble. Log4j is so widely used that millions of applications were affected, and attackers could run their own code remotely to take over systems.
More recent cases follow the same pattern. In 2023, a criminal group used a zero-day in the file transfer software MOVEit Transfer to steal data from thousands of organizations before a patch was available.
Who uses zero-day exploits?
Very different groups use zero-day exploits:
- Cybercriminals: Hacker groups use zero-day exploits to break into networks, steal data or spread ransomware. Most of them are after money, which they make through extortion or by selling stolen data.
- State actors: Many governments use zero-day exploits for espionage or targeted attacks. These actors often have vast resources and technical expertise to deploy specially developed exploits.
- Security researchers: On the positive side, security researchers and ethical hackers actively seek vulnerabilities to report and fix them. Bug bounty programs have contributed to more vulnerabilities being discovered and resolved early.
How are zero-day exploits discovered?
Finding a zero-day exploit is hard work, and artificial intelligence increasingly helps with it. Security researchers, companies and government organizations try to find such threats before they cause damage.
- Proactive security research: Security researchers keep testing software for vulnerabilities. Fuzzing, which feeds a program large amounts of unexpected input automatically, finds many of them.
- Bug bounty programs: Many companies pay researchers for reporting security vulnerabilities. That gives researchers a reason to report a flaw instead of selling it to criminals.
- Modern detection methods: With machine learning, security tools can spot unusual system behavior that may point to a zero-day exploit, which helps catch new attacks early.
Protection against zero-day exploits
You cannot patch a flaw nobody knows about, so protection against zero-day exploits combines technical and organizational measures:
- Regular updates: Keep software up to date. It closes known gaps and shortens the window once a zero-day becomes public.
- Modern security solutions: Systems like intrusion detection systems (IDS) or endpoint detection and response (EDR) help identify suspicious behavior. The same layering idea works for web forms: TrustCaptcha’s CAPTCHA security concept stacks four independent layers against bots, so no single check has to catch everything.
- Security awareness: Employees should be regularly trained to recognize phishing attacks and other common methods that often serve as entry points for zero-day attacks.
Conclusion: how can you strengthen your cybersecurity?
A zero-day exploit hits a flaw nobody has fixed yet, which is why it can go undetected and do a lot of damage. You cannot defend against a specific unknown flaw, but you can make it harder to use one. Install updates quickly, because the WannaCry systems were hit by a flaw that already had a patch. Give users and services only the rights they need, watch systems for unusual behavior with IDS or EDR, and train staff to spot phishing, since that is often how attackers get in. And if you find a vulnerability yourself, report it to the vendor so it stops being a zero-day.