

Rust CAPTCHA Integration
Add a Rust CAPTCHA to your backend to stop bot sign-ups, form spam and API abuse. Our step-by-step Rust integration validates the verification token in minutes. Your users solve no puzzles, data is processed in the EU, and the setup is GDPR-compliant.
Quickstart
How the integration works
1. Create a CAPTCHA
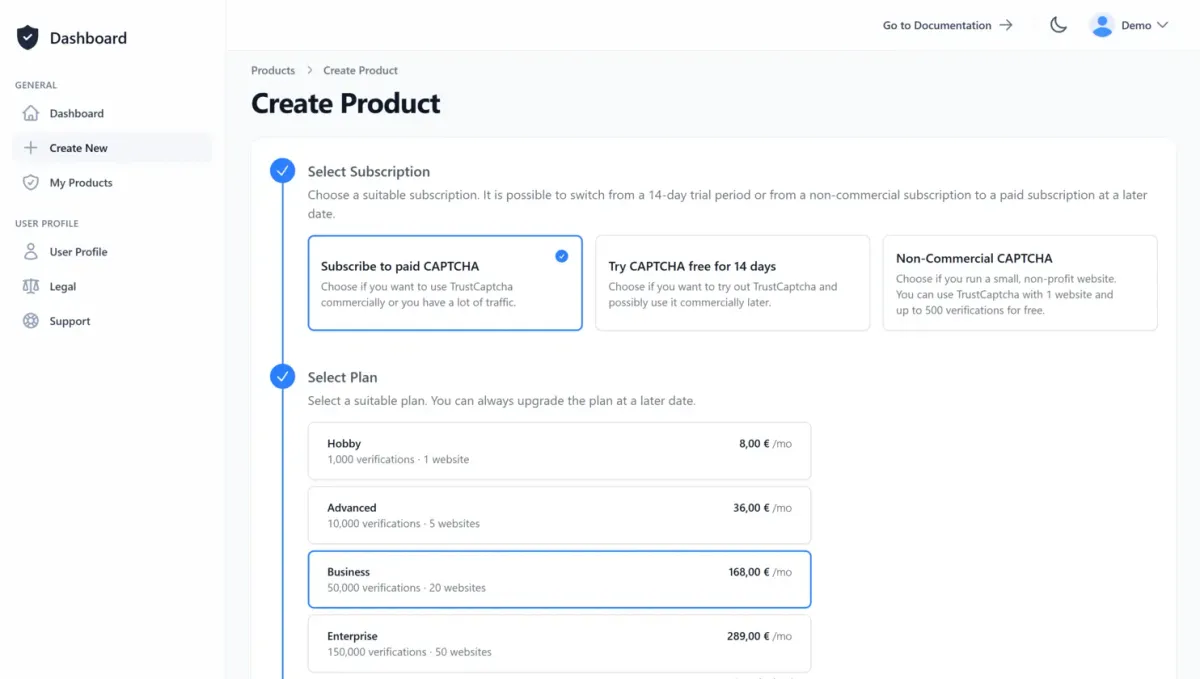
Create a user account or log in with an existing one. Then create a new CAPTCHA or pick an existing one. If you want to try TrustCaptcha first, every plan comes with a 14-day free trial.
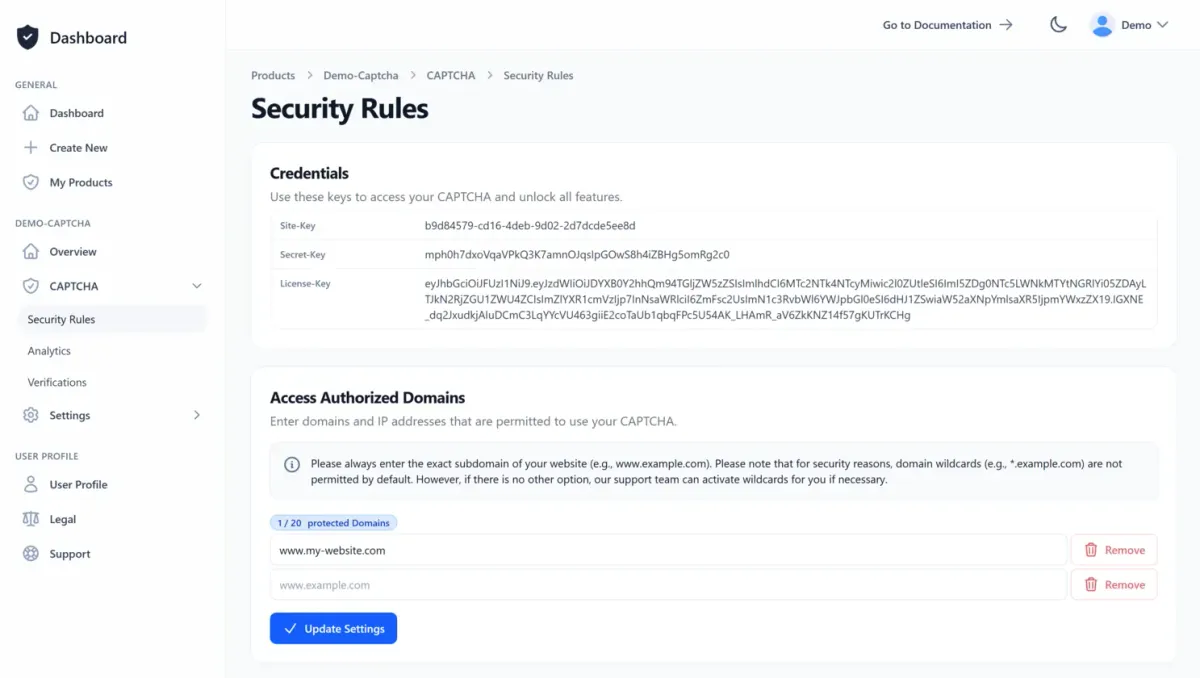
The CAPTCHA overview page shows your site key and license key, and you create your API key there. Add your website’s domains to the authorized domains in the CAPTCHA security rules so they can use your CAPTCHA.
2. Integrate the CAPTCHA widget into your frontend
Integrate the CAPTCHA widget into your website or app. The CAPTCHA widget guide in our documentation has step-by-step instructions.
Read the documentation
The CAPTCHA widget will then be displayed on your website or app:
Pre-built frontend integrations
Our pre-built frontend integrations add the CAPTCHA widget to your website or application. If there is none for your frontend technology yet, your developers can integrate the widget themselves using our documentation or ask our support team for a pre-built integration.

;}.cls-3{fill:%2333c6f4;}.cls-4{fill:%231b447e;}.cls-5{fill:%23fff;}.cls-6{stroke:%23221e1f;stroke-miterlimit:10;stroke-width:7.16px;}%3c/style%3e%3cclipPath%20id='clip-path'%20transform='translate(1.72)'%3e%3ccircle%20class='cls-1'%20cx='119.73'%20cy='119.73'%20r='116.15'/%3e%3c/clipPath%3e%3c/defs%3e%3cg%20id='Layer_2'%20data-name='Layer%202'%3e%3cg%20id='Layer_1'%20data-name='Layer%201'%3e%3cg%20class='cls-2'%3e%3ccircle%20class='cls-3'%20cx='121.45'%20cy='119.73'%20r='116.15'/%3e%3cpath%20class='cls-4'%20d='M239.32,167.79c-53.41-24-108.37-91.46-113-94.55s-10.84.77-10.84.77c-3.87-6.19-10.06.77-10.06.77C76.77,123.55.14,170.11.14,170.11S36.94,237.79,122,237.79C208.48,237.79,239.32,167.79,239.32,167.79Z'%20transform='translate(1.72)'/%3e%3cpath%20class='cls-5'%20d='M67.48,116.58s15.48-7,12.38,4.65-15.48,28.64-11.61,29.41S83,140.58,86.06,142.12s5.42.78,3.87,6.2-3.1,9.29,0,9.29,5.42-7,9.29-13.94,10.06-3.87,12.38-1.55,9.29,15.49,14.71,13.94,8.51-8.52,6.19-24,1.55-20.12,1.55-20.12,4.64-2.32,13.16,8.51,24,27.09,26.31,26.32-10.83-17.8-7.74-19.35,15.48,2.32,21.68,7.74c0,0,2.12,8.87,2.12.36L126.31,73.24,115.47,74l-10.06.77S80.64,111.94,67.48,116.58Z'%20transform='translate(1.72)'/%3e%3cpath%20class='cls-6'%20d='M239.32,170.11c-53.41-24-108.37-93.78-113-96.87s-10.84.77-10.84.77c-3.87-6.19-10.06.77-10.06.77C76.77,123.55.14,170.11.14,170.11'%20transform='translate(1.72)'/%3e%3c/g%3e%3ccircle%20class='cls-6'%20cx='121.45'%20cy='119.73'%20r='116.15'/%3e%3c/g%3e%3c/g%3e%3c/svg%3e)


'/%3e%3c/svg%3e)


3. Validate the CAPTCHA result in your backend
The following steps show how a Rust backend fetches the CAPTCHA verification result from our server and decides what to do with it. For the full instructions, read the CAPTCHA integration guide for Rust in our documentation.
Read the documentation
First, install our TrustCaptcha Rust dependency:
cargo add trustcaptchaFetch the verification result from our server with the verification token and your API key:
// Retrieving the verification result
let trust_captcha = TrustCaptcha::builder("<your_api_key>").build()?;
let verification_result = match trust_captcha.get_verification_result("<verification_token_from_your_client>").await {
  Ok(result) => result,
  Err(e) => {
    // Fetch verification result failed - handle error
    return;
  }
};
Based on the verification result and your own requirements, decide how to proceed:
// Act on the verification result
if !verification_result.verification_passed || verification_result.score > 0.5 {
  // Verification failed or bot score > 0.5 - possible automated request
}
Need detailed information about the Rust CAPTCHA integration?
Our Rust CAPTCHA integration guide has the detailed instructions, and our CAPTCHA samples repository on GitHub has a complete integration example.
Other backend technology instead of Rust?
If you run something other than Rust on your server, or have several backends, pick a different integration here. If we have no pre-built integration for your backend technology yet, your developers can integrate the CAPTCHA verification themselves using our documentation or ask our support team for a pre-built integration.


4. Test your integration
TrustCaptcha is now active. Send a test request and check that it goes through.
FAQs
What do I need to validate a Rust CAPTCHA on my backend?
Do I still need a frontend integration if I use Rust on the backend?
How does the verification token reach my Rust backend?
What do 'verification passed' and 'bot score' mean?
How should I choose a decision threshold for the bot score?
How long is a verification token valid, and what happens if the API is not reachable?
TrustCaptcha blocks spam and bots, not customers. No puzzles, GDPR-compliant, EU-hosted.
Protect your Rust application with TrustCaptcha in just a few steps!
- EU-hosted & GDPR-compliant
- No puzzles
- Try free for 14 days